A contact form is supposed to be easy to reach. So is the lead form on your new Lovable app. The same open door that lets a prospective customer write to you also lets bots send junk into your inbox, database, and CRM.

Adding a CAPTCHA makes every visitor do extra work. But leaving the form alone means sorting through fake inquiries and wondering which message was real.

Today, ActiveLayer offers a guided spam-protection setup for Lovable forms. Copy our prompt into your existing project, let Lovable inspect its real submission paths, and review the server-side changes before you publish. This is a project-specific implementation, not a switch that automatically protects every app built with Lovable.

How Lovable spam protection works

Your public contact and lead forms

Start with an existing public form that a visitor can submit, such as a contact, inquiry, or lead form. The Lovable setup page provides a prompt for these forms and asks Lovable to report which ones it actually protected. Check that report for your app rather than assuming every form is covered.

Lovable must inspect each form’s fields and the path that actually handles its submission. A form that writes directly from the browser to a database needs a server handler for the protected write. An alternate endpoint or database policy must not let the same submission bypass the check. The guide tells Lovable to reuse your existing backend and keep the form’s design, validation, accessibility, and normal delivery path intact.

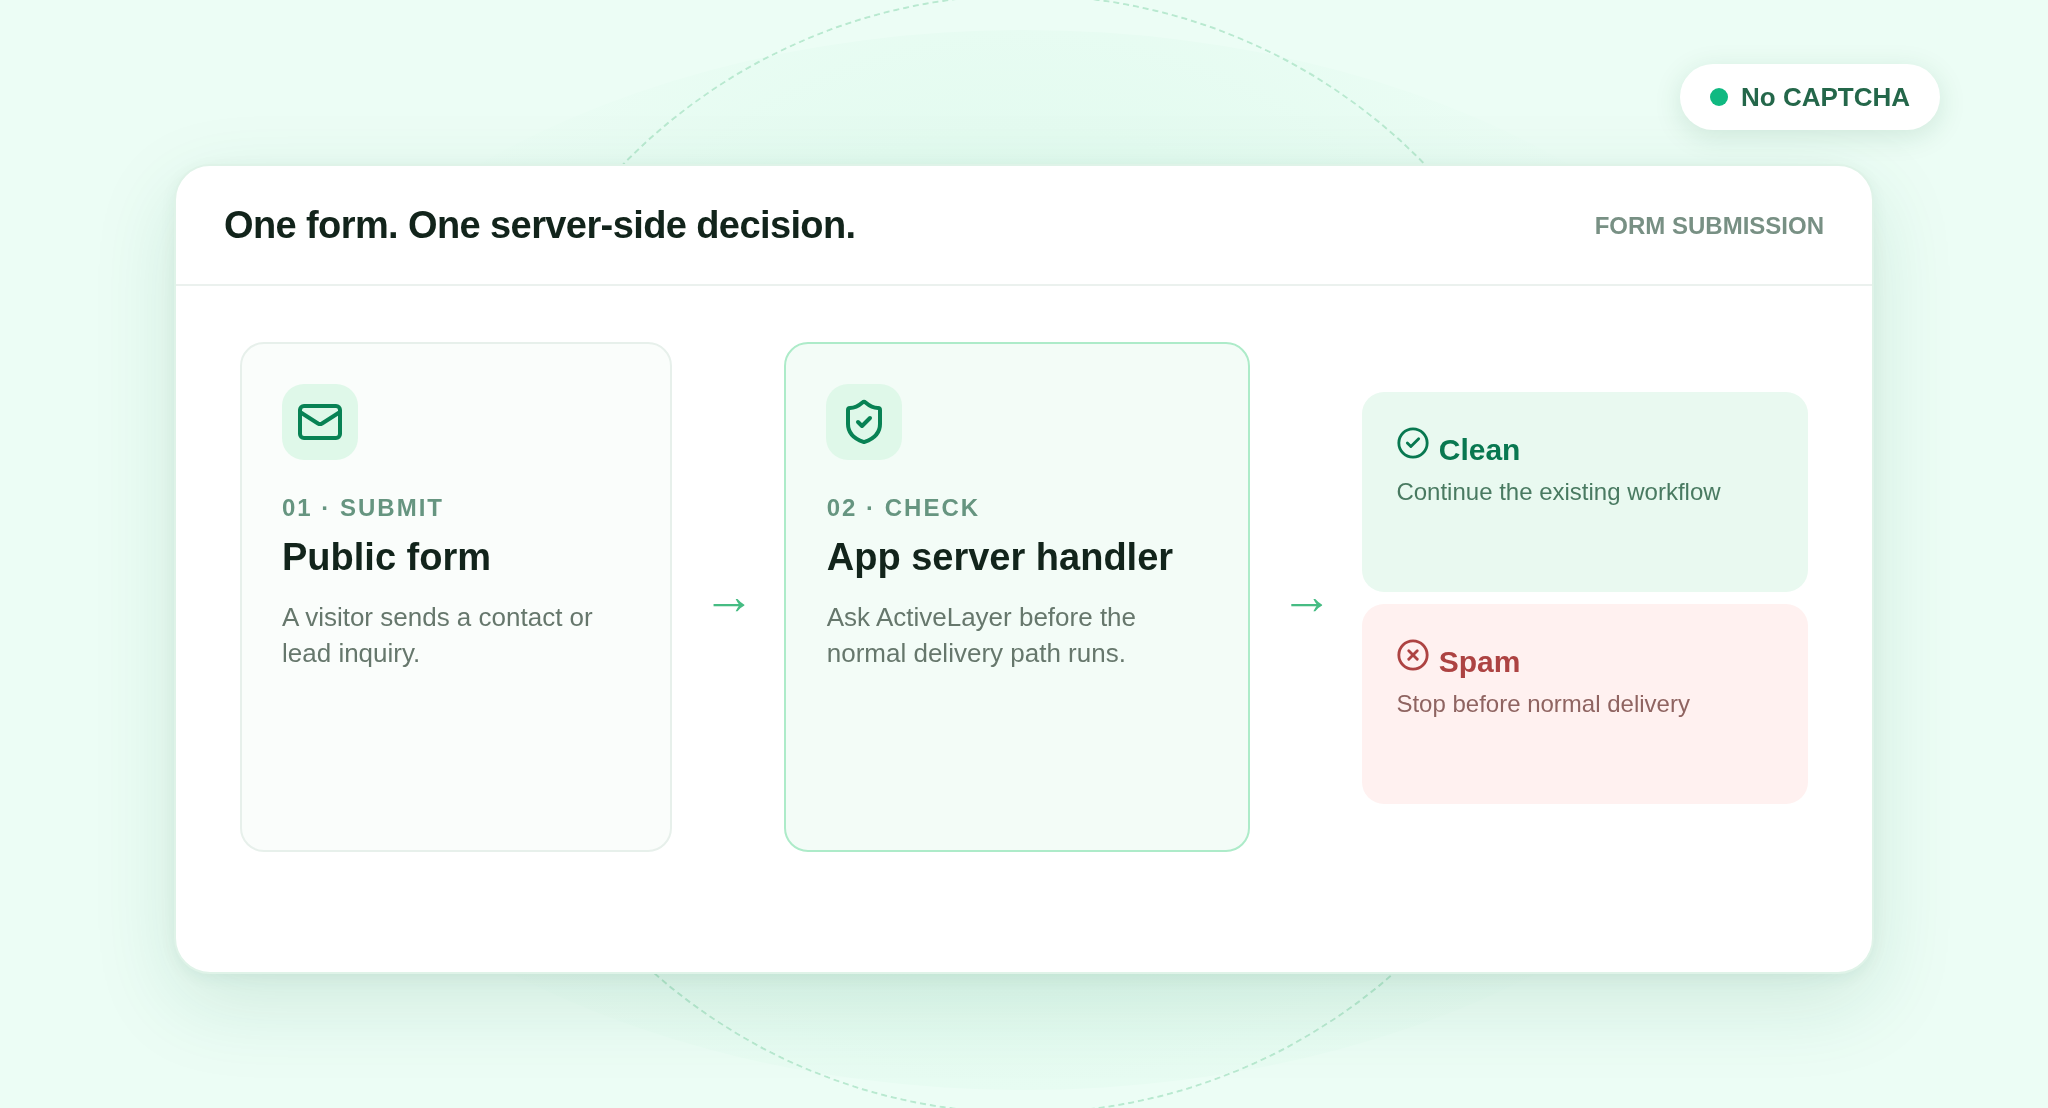
The integration guide directs Lovable to put the check in your app’s server handler after form validation and before saving a lead, sending an email, calling a CRM, or queuing other work. The handler sends mapped visitor content to ActiveLayer and reads the API’s is_spam verdict. When implemented as described, a clean verdict follows the existing submission path once. A spam verdict stops that path and returns a form error with the input preserved. The exact wording depends on your app. Review and test the generated changes to make sure your form follows this path.

This recipe does not cover login, account creation, password reset, payments, or uploads. An embedded form whose submission backend you cannot modify needs its own provider-side integration. Do not call it protected because its page happens to be inside a Lovable app.

Diagram of a protected public form passing through its server handler to an ActiveLayer spam verdict before normal delivery
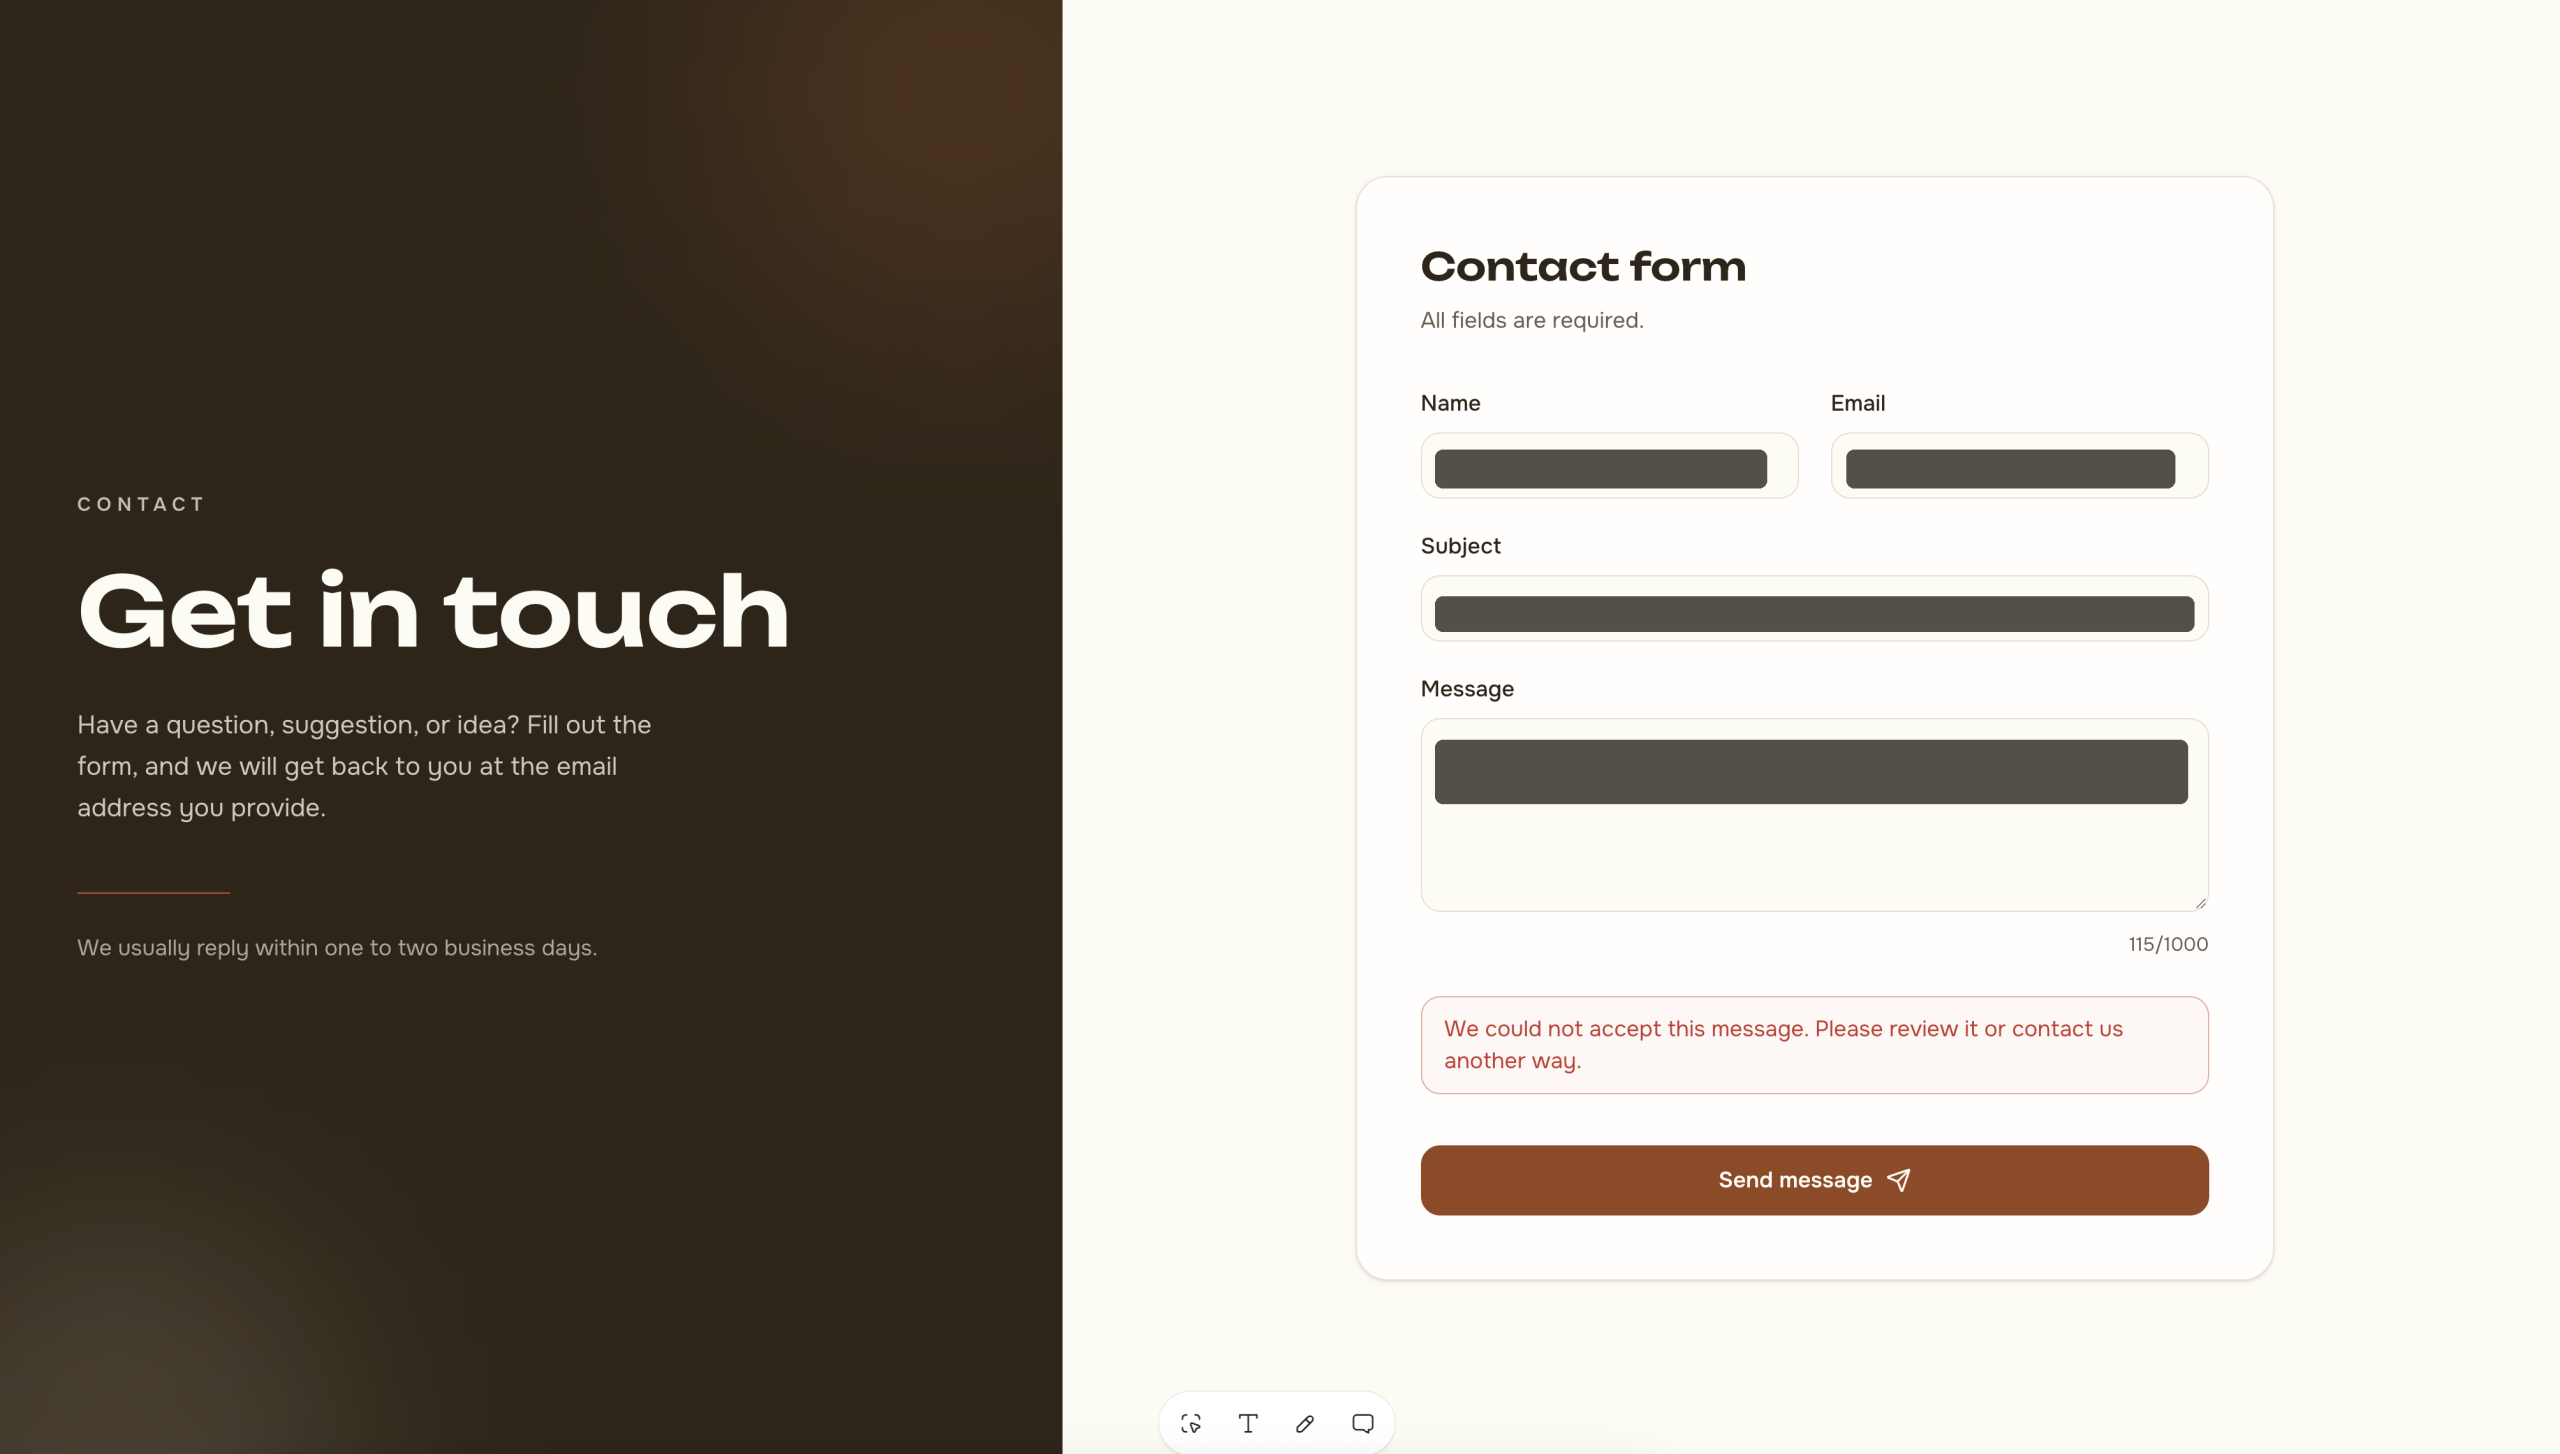
A Lovable demo contact form displaying an inline message after a blocked test submission; entered test data redacted
Example: a blocked contact-form test in Lovable preview. Test data redacted; form design and message vary by project.

What happens when a check is unavailable

The published guide specifies a fail-open default for a timeout, service error, or exhausted allowance. It tells the implementer to continue the normal submission path, record the attempt as unchecked, and surface the problem to the owner. Unchecked is not a clean verdict: spam can get through while checks are unavailable. The guide handles a payload validation error differently, stopping the submission for repair while retaining the visitor’s input. If your app already has an explicitly stricter policy, the guide says to preserve it. Confirm the implemented behavior in your own project.

Why Lovable spam protection skips the CAPTCHA

A prospective customer should not have to solve a puzzle to ask for a quote. This setup calls ActiveLayer from your app’s server handler, not from a visible CAPTCHA widget. Your visitor keeps the form they came to fill out. If the check returns a spam verdict, they see your app’s form error rather than a challenge; if it returns a clean verdict, the form behaves as it did before.

Server-side also matters for the API key. It belongs in Lovable’s secure secret input or your connected backend’s secret manager, never in project chat, a browser variable, or frontend source. Your browser talks to your own submission handler; that handler talks to ActiveLayer. The guide asks the implementer to test not just the happy path but blocked verdicts, API failures, field mapping, and bypass routes. A preview test alone does not establish that the published app is protected.

Set it up in three steps

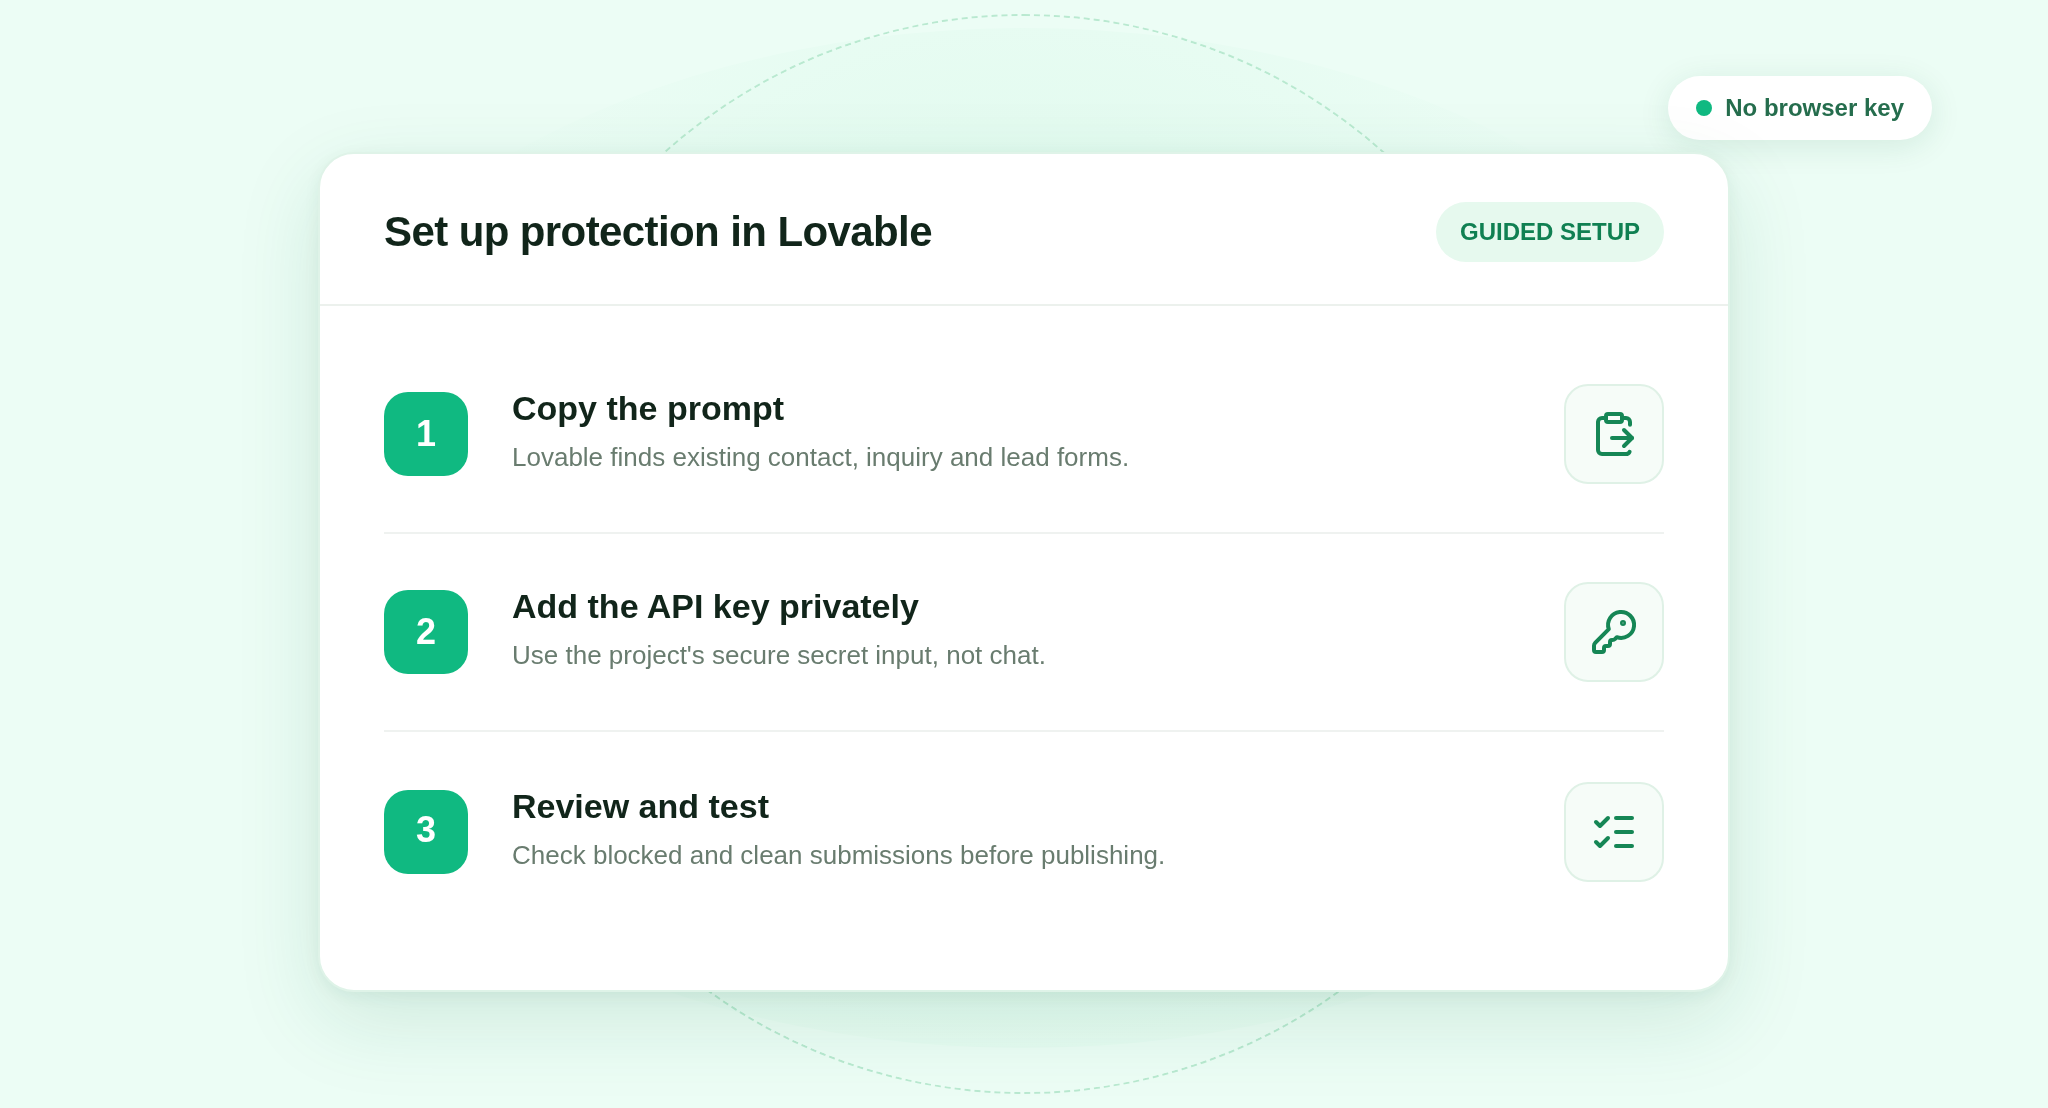
1. Paste the prompt into your existing Lovable project. Open the ActiveLayer for Lovable page, copy the full prompt, and give it to Lovable. It links to the implementation guide and asks Lovable to report which forms it found, how it mapped them, and any paths it cannot protect. This is not the ActiveLayer WordPress plugin.

2. Add your API key privately. Create a key in your ActiveLayer account. When Lovable requests ACTIVELAYER_API_KEY, use its secure secret input. Do not paste the key into chat. The guide requires a server-side credential check before setup is called complete.

3. Review, test, and publish. Inspect Lovable’s edits. Submit a normal form, simulate a blocked verdict and an API failure, and check that an old public route cannot write around the new handler. Test the published app after deployment, not just its preview. Ask Lovable to identify any form left unprotected. The server implementation depends on your project’s runtime and backend.

Three-step Lovable setup diagram: copy the prompt, add a server-side API key, and review and test the form

A note for agencies

If you build Lovable apps for clients, document coverage separately for each project. The same prompt is a starting point, not evidence that every client’s form uses the same handler. ActiveLayer’s pricing page lists unlimited sites on its plans; usage is counted in checks. Keep each project’s key in its server-side secret store and verify its live submission path before handing it over.

Pricing

New signups can start with 200 checks in total, a one-time allowance, with no credit card required. Existing Free accounts may have a different allowance shown in their account. Paid plans are available as your check volume grows. Check the current options on the pricing page.

Get started

Open your Lovable project, copy the prompt, and check the changes it makes to the forms that matter to you. The goal is specific: a server-side decision before a public inquiry becomes an email or lead, while legitimate visitors keep the form they came to use.

Questions? Reach out.

Integration

Introducing ActiveLayer for FunnelKit

ActiveLayer hero: 'Native Spam Protection for FunnelKit' on a green grid banner with logo and a New Integration tag at top right.

FunnelKit spam protection comes down to one thing: the opt-in form. It is built to be public. Anyone can land on your squeeze page, drop in an email, and become a lead. Bots count on it.

Fake leads do more than pad your numbers. They poison your list, skew your funnel stats, trip your automations, and burn send volume on inboxes that were never real. Every junk opt-in is another contact you scrub by hand, and another welcome sequence sent to nobody.

The usual answer is a CAPTCHA. Make every new lead prove they are human before they can opt in. The trouble is what that costs you. CAPTCHA challenges can interrupt form completion.

There is a better place to catch them.

Today, ActiveLayer ships native FunnelKit spam protection. Every opt-in is scored by AI on the server, before the lead is ever created. No puzzles. No checkboxes. Real subscribers never see a thing.

How FunnelKit spam protection works

1. The opt-in form

Your opt-in form is the one element of a funnel that has to stay open to strangers. That is the whole point of it, and it is exactly why bots target it. The fields are predictable, the URL is public, and a successful submit creates a real lead. A lead-capture form is a chokepoint. So we guard it.

When someone submits your opt-in, ActiveLayer scores it on the server in the same request. The check is synchronous, so the verdict comes back before FunnelKit writes the lead. A clean opt-in goes through untouched and the contact is created as normal. A spam opt-in is stopped cold: the form re-renders with an inline error, and no lead and no contact record are ever written.

A few details we cared about:

  • ActiveLayer runs after FunnelKit finishes its own validation, not before. If FunnelKit already rejected the submission, we don’t waste an API call second-guessing it.
  • It covers the opt-in step whether the form is embedded on the page or opens as a two-step pop-up. Same gate either way.
  • The blocked visitor sees a plain message, “Your submission was flagged as spam. Please try again or contact support.” No stack trace, no clue about what tripped it.

This integration protects FunnelKit lead-capture forms. Checkout is outside its scope; ActiveLayer does not gate a purchase.
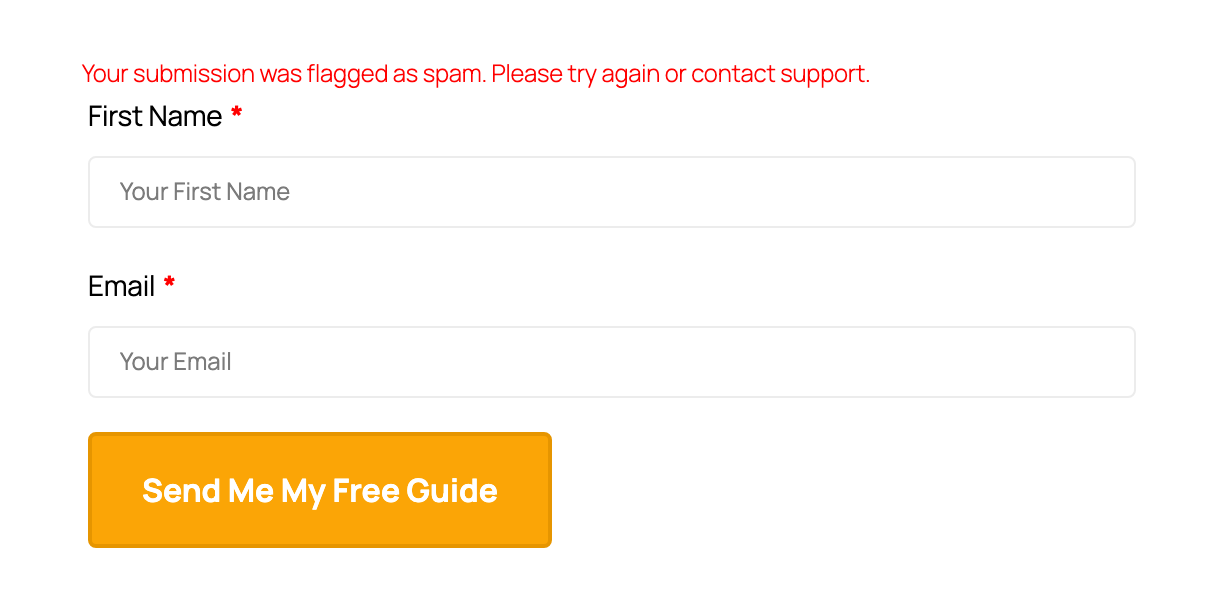
FunnelKit opt-in form showing an inline error blocking a fake lead submission

2. The Submissions log

A spam filter you can’t see is a spam filter you can’t trust. If something blocks a real subscriber at your opt-in, that’s a lead you lost and never heard about. So ActiveLayer shows its work.

Every opt-in it processes lands in the Submissions log, blocked or clean. Open ActiveLayer → Submissions and each opt-in is right there. The provider column reads FunnelKit, with the opt-in’s form name beside it, so you can tell funnel opt-ins from your contact-form traffic at a glance. You see the verdict on each one. Open any entry for the score and the signals behind it.

Three things worth knowing:

  • Clean opt-ins are logged too, not just the blocks. You get the full picture of who tried to subscribe, not a one-sided list of rejects.
  • If a real subscriber ever gets caught, open the entry and report it. ActiveLayer retrains on that signal, so the same mistake gets less likely over time.
  • Every row shows the email submitted, so a blocked opt-in is an address you can actually look up, not an anonymous counter.

You audit the door instead of trusting it blindly. That’s the difference between a tool that works and a tool that says it does.
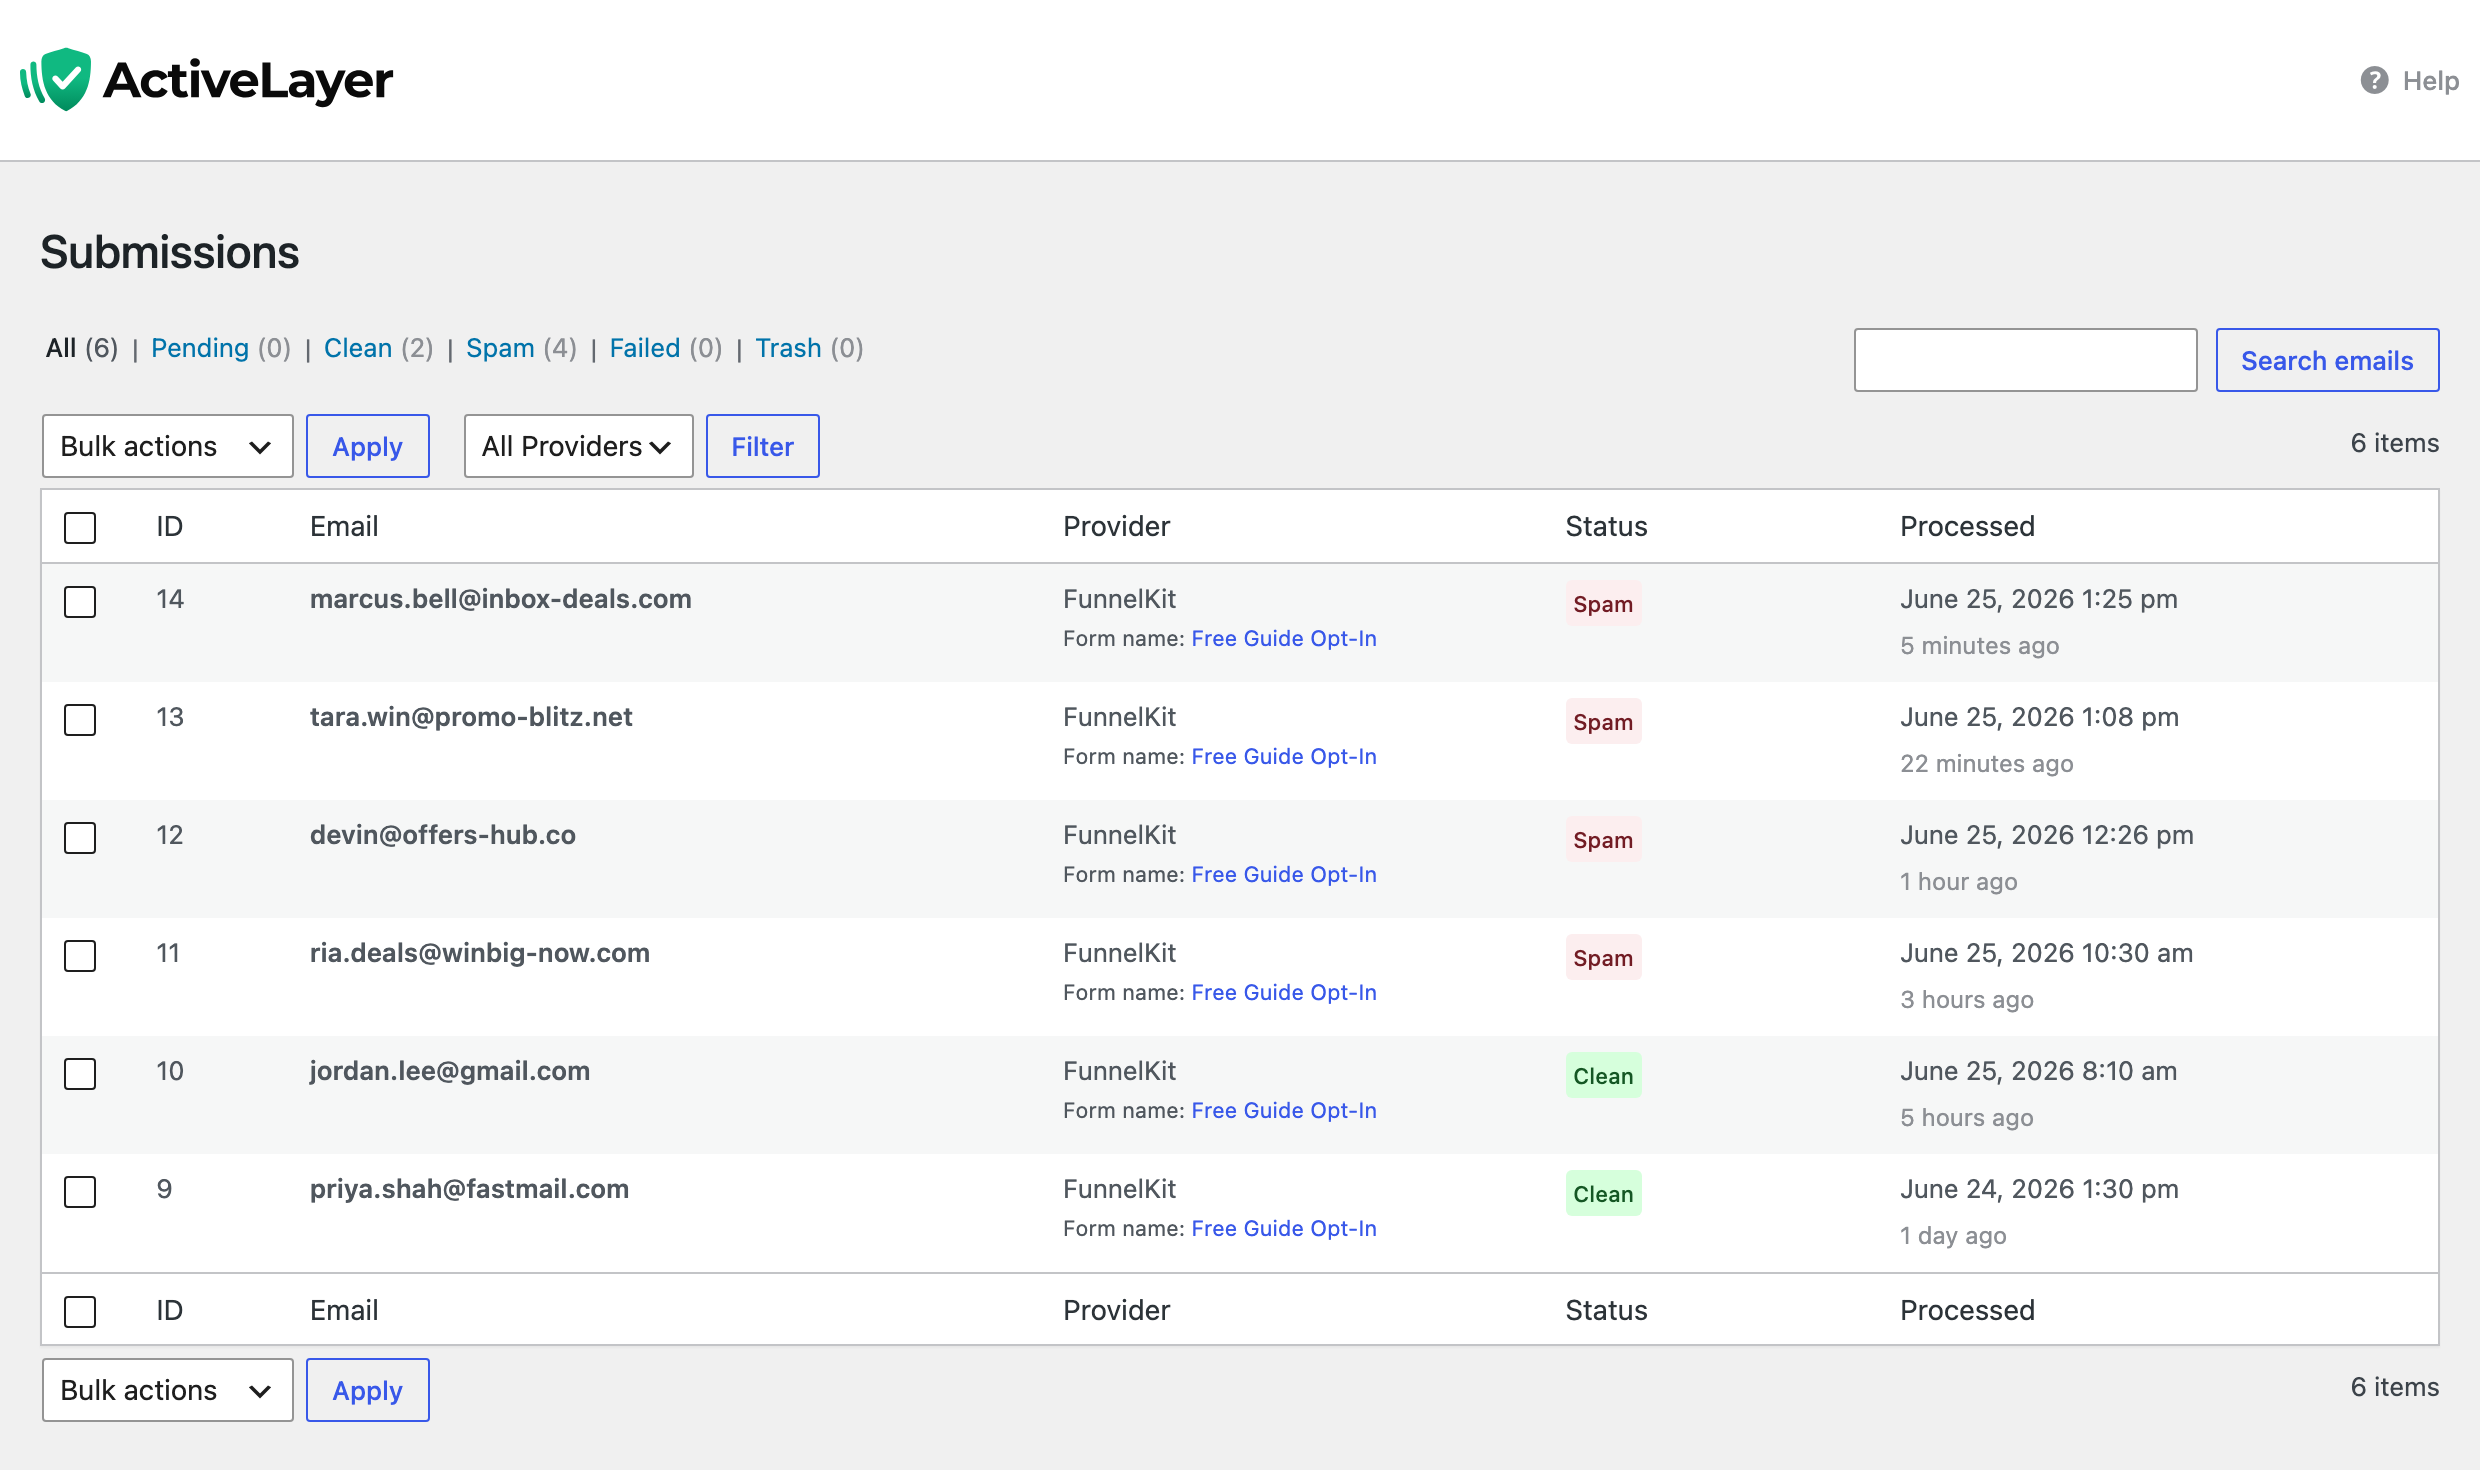
ActiveLayer Submissions log showing blocked and clean FunnelKit opt-in attempts, each tagged with the FunnelKit provider and form name

Why FunnelKit spam protection skips the CAPTCHA

An opt-in is a high-intent moment. Someone decided your offer is worth their email. That is the worst possible time to hand them a puzzle. CAPTCHA challenges can interrupt form completion.

ActiveLayer does its work entirely server-side. There is no challenge to render, no widget to load, no third party watching your visitors. The plugin drops a few hidden signal fields into the opt-in, invisible to visitors, and the verdict happens on our API. Your form looks exactly like it did yesterday.

Three properties matter here:

  • The check is synchronous and runs in the right order, after FunnelKit validates and before the lead exists. A blocked bot never becomes a contact in your list.
  • It fails open. If our API is slow or unreachable, the opt-in proceeds as if the check passed. ActiveLayer never blocks a real lead because we had a bad afternoon.
  • It does nothing until you connect a key, then it blocks on spam by default. No tracking-only half-measures, because letting a known bot through would create a junk contact you have to clean up.

Most spam tools start by suspecting your visitors. We start from the other direction. Never block a real lead. Catch the bots at the door.

FunnelKit spam protection in three steps

Setup is the same shape as every other ActiveLayer install.

1. Install the ActiveLayer plugin. It’s free on the WordPress plugin directory. Activate it like any other plugin.

2. Paste your API key. Sign up at app.activelayer.com for 200 free checks, no credit card. Paste the key into the plugin settings.

3. There is no step three. FunnelKit protection is on by default the moment your key connects. You’ll see FunnelKit marked Active under ActiveLayer → Integrations, with a toggle if you ever want to turn it off.

That’s the whole setup. The next bot that hits your opt-in gets stopped, and you don’t lift a finger.

A note for agencies

One ActiveLayer account covers every client funnel you run. Every plan includes unlimited sites, and you’re billed by check volume, not by how many installs you manage. Add a funnel site, drop in the key, done.

That’s the part our agency customers asked us to keep simple. We did.

Pricing

Same plans as everywhere else. Nothing new to buy for FunnelKit spam protection.

  • Free: 200 spam checks in total, unlimited sites, full API access, no credit card.
  • Pro: from $5/month for 5,000 checks, scaling up to 250,000. Unlimited sites. Email support.
  • Enterprise: from $149/month for 500,000+ checks, custom SLA, SSO, dedicated support.

One blocked spam run can mean hundreds of junk leads and a poisoned automation in an afternoon. The monthly fee costs less than the time you’d spend cleaning that up by hand.

Get started

Install ActiveLayer, connect your key, and FunnelKit spam protection is live by the time you finish your coffee. No CAPTCHA to configure, nothing to tune.

Already running ActiveLayer on your contact forms? Then there’s truly nothing to do. The same key already turns on FunnelKit spam protection, on by default, the moment you update.

Questions about your funnel’s specific setup? Reach out. We read every message, and our team will help you get this running.

Get Started

ActiveLayer Team

We build the spam detection behind ActiveLayer — studying how bots actually reach forms, comments and signups, and shipping what stops them.

Eliminate Spam. Protect Every Lead.
It’s That Simple.

Join the thousands of website owners, agencies, and developers who use ActiveLayer to stop spam and protect every real submission.

Get Started for Free
  • 200 checks for free
  • Setup in minutes
  • No credit card required
Integration

Introducing ActiveLayer for MemberPress

ActiveLayer for MemberPress: native spam protection for membership signups, no CAPTCHAs

MemberPress spam protection comes down to one page: the checkout. It stays open to strangers by design. Anyone can load your registration form, type an email, and create a WordPress account. Bots count on it.

Fake signups do more than pad your member count. They poison your member list, burn through coupon codes, and trip payment flows you then have to refund. Every junk account is another row you clean up by hand, and another welcome email sent to nobody.

The usual answer is a CAPTCHA. Make every new member prove they are human before they can join. The trouble is what that costs you. CAPTCHA challenges can interrupt form completion.

There is a better place to catch them.

Today, ActiveLayer ships native MemberPress spam protection. Every membership signup is scored by AI on the server, before the WordPress account and the membership are ever created. No puzzles. No checkboxes. Real members never see a thing.

How MemberPress spam protection works

1. The public signup form

Your membership checkout is the one page that has to stay open to strangers. That is the whole point of it, and it is exactly why bots target it. The fields are predictable, the URL is public, and a successful submit creates a real WordPress user. A registration form is a chokepoint. So we guard it.

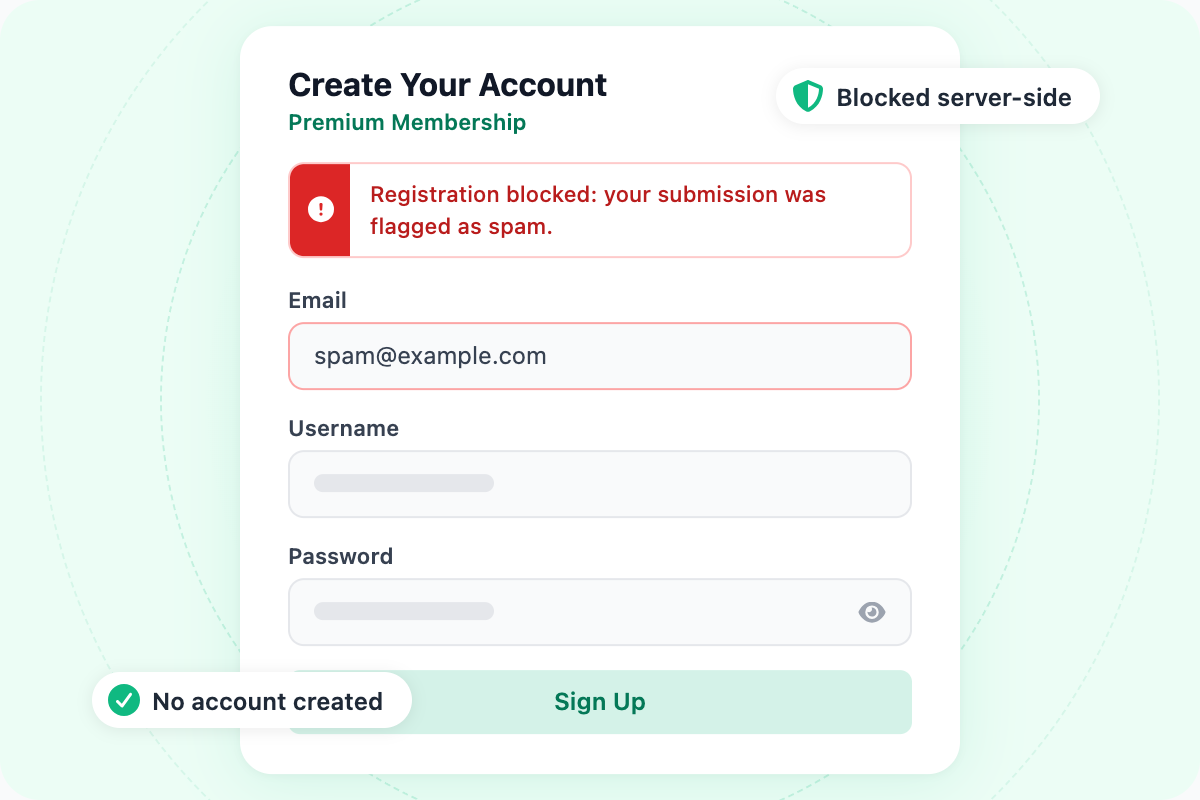
When someone submits your signup form, ActiveLayer scores it on the server in the same request. The check is synchronous, so the verdict comes back before MemberPress creates the account. A clean signup goes through untouched and the membership activates as normal. A spam signup is stopped cold: the checkout re-renders with an inline error, and no WordPress user and no membership record are ever written.

It covers the classic form, Single Page Checkout, and ReadyLaunch. Free, free-trial, and fully discounted signups are checked by default. Paid signups require an opt-in setting.

MemberPress membership checkout showing an inline error blocking a fake registration attempt

2. The Submissions log

A spam filter you can’t see is a spam filter you can’t trust. If something blocks a real customer at your checkout, that’s a sale you lost and never heard about. So ActiveLayer shows its work.

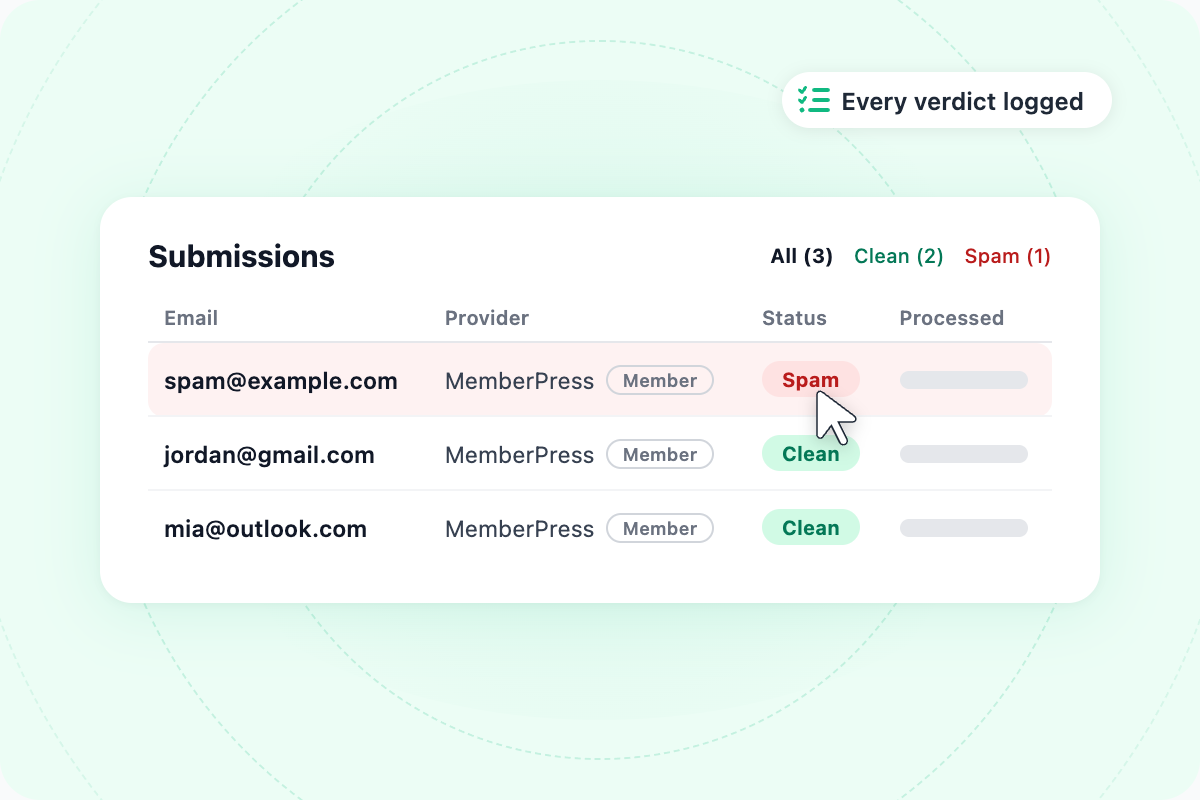
Every signup it processes lands in the Submissions log, blocked or clean. Open ActiveLayer → Submissions and each membership signup is right there, tagged Member so you can tell registrations apart from your contact-form traffic at a glance. The provider column reads MemberPress. You see the verdict, the score, and the signals behind it.

Three things worth knowing:

  • Clean signups are logged too, not just the blocks. You get the full picture of who tried to join, not a one-sided list of rejects.
  • If a real member ever gets caught, open the entry and report it. ActiveLayer retrains on that signal, so the same mistake gets less likely over time.
  • Membership rows show the username or email, so a blocked signup is a name you can actually look up, not an anonymous counter.

You audit the door instead of trusting it blindly. That’s the difference between a tool that works and a tool that says it does.

ActiveLayer Submissions log showing a blocked MemberPress signup attempt labelled as Member

Why MemberPress spam protection skips the CAPTCHA

A signup is the highest-intent moment you get. Someone decided your membership is worth their email and, often, their card. That is the worst possible time to hand them a puzzle. CAPTCHA challenges can interrupt form completion.

ActiveLayer does its work entirely server-side. There is no challenge to render, no widget to load, no third party watching your members. The plugin drops a few hidden signal fields into the checkout, invisible to visitors, and the verdict happens on our API. Your form looks exactly like it did yesterday.

Three properties matter here:

  • The check is synchronous and runs in the right order, after MemberPress validates and before the account exists. A blocked bot never becomes a row in your users table.
  • It fails open. If our API is slow or unreachable, the signup proceeds as if the check passed. ActiveLayer never blocks a legitimate registration because we had a bad afternoon.
  • It does nothing until you connect a key, then it blocks on spam by default. No tracking-only half-measures on account creation, because letting a known bot register would create a real account you have to clean up.

Most spam tools start by suspecting your visitors. We start from the other direction. Never block a real member. Catch the bots at the door.

MemberPress spam protection in three steps

Setup is the same shape as every other ActiveLayer install.

1. Install the ActiveLayer plugin. It’s free on the WordPress plugin directory. Activate it like any other plugin.

2. Paste your API key. Sign up at app.activelayer.com for 200 free checks, no credit card. Paste the key into the plugin settings.

3. There is no step three. MemberPress protection is on by default the moment your key connects. You’ll see MemberPress marked Active under ActiveLayer → Integrations, with a toggle if you ever want to turn it off.

That’s the whole setup. The next bot that hits your checkout gets stopped, and you don’t lift a finger.

A note for agencies

One ActiveLayer account covers every client site you run. Every plan includes unlimited sites, and you’re billed by check volume, not by how many installs you manage. Add a membership site, drop in the key, done.

That’s the part our agency customers asked us to keep simple. We did.

Pricing

Same plans as everywhere else. Nothing new to buy for MemberPress spam protection.

  • Free: 200 spam checks in total, unlimited sites, full API access, no credit card.
  • Pro: from $5/month for 5,000 checks, scaling up to 250,000. Unlimited sites. Email support.
  • Enterprise: from $149/month for 500,000+ checks, custom SLA, SSO, dedicated support.

One blocked spam ring can mean dozens of fake accounts and refund headaches in an afternoon. The monthly fee costs less than the time you’d spend cleaning that up by hand.

Get started

Install ActiveLayer, connect your key, and MemberPress spam protection is live by the time you finish your coffee. No CAPTCHA to configure, nothing to tune.

Already running ActiveLayer on your contact forms? Then there’s truly nothing to do. The same key already turns on MemberPress spam protection, on by default, the moment you update.

Questions about your membership site’s specific setup? Reach out. We read every message, and our team will help you get this running.
Get Started

ActiveLayer Team

We build the spam detection behind ActiveLayer — studying how bots actually reach forms, comments and signups, and shipping what stops them.

Eliminate Spam. Protect Every Lead.
It’s That Simple.

Join the thousands of website owners, agencies, and developers who use ActiveLayer to stop spam and protect every real submission.

Get Started for Free
  • 200 checks for free
  • Setup in minutes
  • No credit card required
Integration

Introducing ActiveLayer for AffiliateWP

ActiveLayer for AffiliateWP, native spam protection for the affiliate registration form

AffiliateWP spam protection comes down to one form: the affiliate registration page. It stays open to strangers by design. Anyone can load it, type a name and an email, and apply to your program. Bots count on it.

Fake affiliates do more than pad a list. They poison your referral stats, fish for coupon codes, and clutter the affiliate dashboard you use to run the program. Every junk application is another row you review by hand, and another approval queue you stop trusting.

The usual answer is a CAPTCHA. AffiliateWP ships a honeypot and one optional puzzle, and no native Akismet or CleanTalk hook on that form. So the bots that learned to read CAPTCHAs walk right through, and the people who hate them quietly give up.

There is a better place to catch them.

Today, ActiveLayer ships native spam protection for AffiliateWP. Every affiliate registration is scored by AI on the server, before the affiliate row and the WordPress user are ever created. No puzzles. No checkboxes. Real applicants never see a thing.

How ActiveLayer stops AffiliateWP registration spam

1. The public affiliate registration form

Your affiliate registration form is the one page that has to stay open to strangers. That is the whole point of it, and exactly why bots target it. The fields are predictable, the URL is public, and a successful submit creates a real affiliate and a real WordPress user. A registration form is a chokepoint. So we guard it.

When someone applies to your program, ActiveLayer scores the submission on the server in the same request. The check is synchronous, so the verdict comes back before AffiliateWP creates the account. A clean application goes through untouched and the affiliate is created as normal. A spam application is stopped cold: the form re-renders with an inline error, and no affiliate row and no WordPress user are ever written.

A few details we cared about:

  • ActiveLayer runs after AffiliateWP finishes its own validation, not before. If AffiliateWP already rejected the submission with its honeypot, its CAPTCHA, or a bad email, we don’t waste an API call second-guessing it.
  • It covers both render paths. Whether your registration form comes from the [affiliate_registration] shortcode or the block-based form, the same hidden signal fields and the same gate apply.
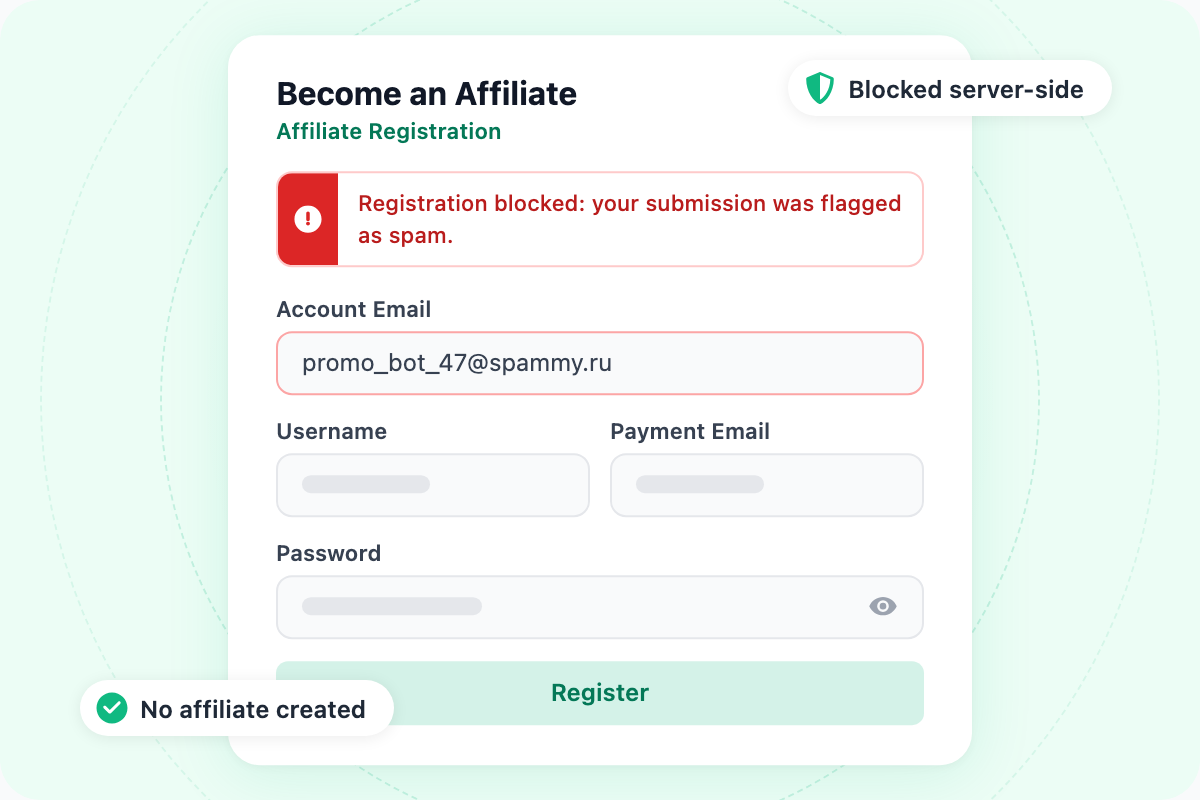
  • The blocked applicant sees a plain message, “Registration blocked: your submission was flagged as spam.” No stack trace, no clue about what tripped it.

And the scope, stated plainly: this release protects your public affiliate registration form, full stop. The affiliate login form, AffiliateWP add-on registration forms (WPForms, Gravity Forms, the other builders), and affiliates that get auto-registered when you let new WordPress users become affiliates automatically are out of scope for this release. We started at the front door on purpose. The registration form is where affiliate spam begins, and a bot that never gets an affiliate account never reaches your dashboard. This release does not score referral or coupon fraud, either. That is a separate problem from spam, and it belongs to AffiliateWP’s own roadmap.

AffiliateWP affiliate registration form showing an inline error blocking a fake affiliate signup attempt

2. The Submissions log

A spam filter you can’t see is a spam filter you can’t trust. If something blocks a real applicant on your registration form, that is a partner you lost and never heard about. So ActiveLayer shows its work.

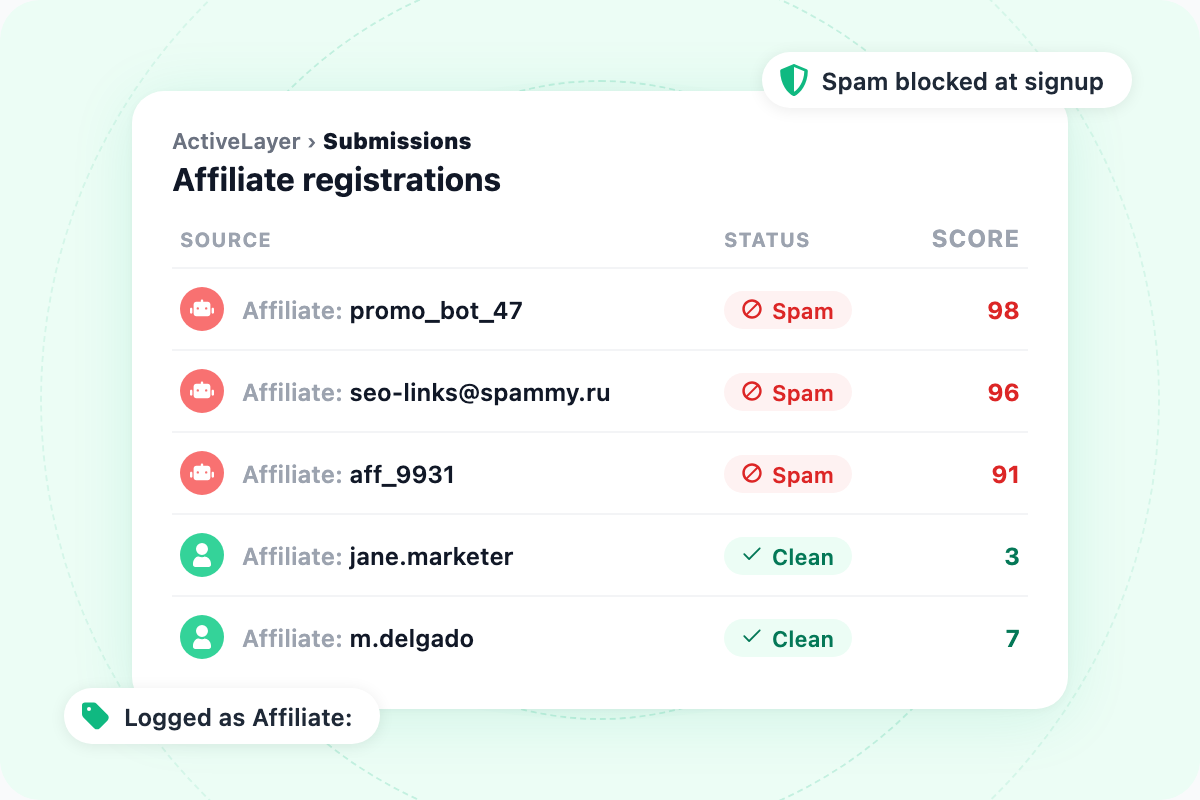
Every registration it processes lands in the Submissions log, blocked or clean. Open ActiveLayer → Submissions and each affiliate application is right there. The form column reads Affiliate: followed by the username or email, because there is no named form to point at, just the one global registration flow. You see the verdict, the score, and the signals behind it.

Three things worth knowing:

  • Clean applications are logged alongside the blocks. You get the full picture of who tried to join, not a one-sided list of rejects.
  • If a real applicant ever gets caught, open the entry and report it. ActiveLayer retrains on that signal, so the same mistake gets less likely over time.
  • Each row carries the attempted username or email, so a blocked application is a name you can actually look up, not an anonymous counter.

You audit the door instead of trusting it blindly. That’s the difference between a tool that works and a tool that says it does.

ActiveLayer Submissions log showing a blocked AffiliateWP affiliate registration labelled with the attempted username

Why we built this without CAPTCHAs

An affiliate application is a high-intent moment. Someone decided your program is worth their time. That is a poor time to hand them a puzzle. Drop the CAPTCHA and you keep the applicants it was quietly costing you, the ones who give up rather than count traffic lights.

ActiveLayer does its work entirely server-side. There is no challenge to render, no widget to load, no third party watching your applicants. The plugin drops a few hidden signal fields into the registration form, invisible to visitors, and the verdict happens on our API. Your form looks exactly like it did yesterday.

Three properties matter here:

  • The check is synchronous and runs in the right order, after AffiliateWP validates and before the affiliate exists. A blocked bot never becomes a row in your affiliates table or your users table.
  • It fails open. If our API is slow or unreachable, the application proceeds as if the check passed. ActiveLayer never blocks a legitimate signup because we had a bad afternoon.
  • It does nothing until you connect a key, then it blocks on spam by default. No tracking-only half-measures on account creation, because letting a known bot register would create a real affiliate you then have to clean up.

Most spam tools start by suspecting your visitors. We start from the other direction. Never block a real applicant. Catch the bots at the door.

AffiliateWP registration spam, gone in three steps

Setup is the same shape as every other ActiveLayer install.

1. Install the ActiveLayer plugin. It’s free on the WordPress plugin directory. Activate it like any other plugin.

2. Paste your API key. Sign up at app.activelayer.com for 200 free checks, no credit card. Paste the key into the plugin settings.

3. There is no step three. AffiliateWP protection is on by default the moment your key connects. You’ll see AffiliateWP marked Active under ActiveLayer → Integrations, with a single toggle if you ever want to turn it off.

That’s the whole setup. The next bot that applies gets stopped, and you don’t lift a finger.

A note for agencies

One ActiveLayer account covers every client site you run. Every plan includes unlimited sites, and you’re billed by check volume, not by how many installs you manage. Add an affiliate program, drop in the key, done.

That’s the part our agency customers asked us to keep simple. We did.

Pricing

Same plans as everywhere else. Nothing new to buy for AffiliateWP.

  • Free: 200 spam checks in total, unlimited sites, full API access, no credit card.
  • Pro: from $5/month for 5,000 checks, scaling up to 250,000. Unlimited sites. Email support.
  • Enterprise: from $149/month for 500,000+ checks, custom SLA, SSO, dedicated support.

One blocked spam run can mean dozens of fake affiliates and a poisoned referral report in an afternoon. The monthly fee costs less than the hours you’d spend cleaning that up by hand.

Get started

Install ActiveLayer, connect your key, and AffiliateWP spam protection is live by the time you finish your coffee. No CAPTCHA to configure, nothing to tune.

Already running ActiveLayer on your contact forms? Then there’s truly nothing to do. The same key already turns on AffiliateWP spam protection, on by default, the moment you update.

Questions about your affiliate program’s specific setup? Reach out. We read every message, and our team will help you get this running.
Get Started

ActiveLayer Team

We build the spam detection behind ActiveLayer — studying how bots actually reach forms, comments and signups, and shipping what stops them.

Eliminate Spam. Protect Every Lead.
It’s That Simple.

Join the thousands of website owners, agencies, and developers who use ActiveLayer to stop spam and protect every real submission.

Get Started for Free
  • 200 checks for free
  • Setup in minutes
  • No credit card required
Integration

Introducing ActiveLayer for WS Form

ActiveLayer for WS Form: native spam protection for form submissions

WS Form spam protection comes down to one moment: what happens after someone hits submit. The entry gets written to your database. Your form actions fire. Notification emails go out, webhooks ping your CRM, and your team gets paged about a lead that was never real.

That is the part that costs you. A junk entry is one more row to sift through, one more email you learn to ignore, one more integration call you pay for. The forms doing the damage are the everyday ones: contact forms, lead forms, signup forms, the payment form on your pricing page. The ones you actually need open to the public.

The usual answer is a CAPTCHA bolted onto every form. It nags the real people filling out your forms, and the bots that learned to read puzzles submit anyway. You lose the visitor and keep the spam.

There is a better place to catch them.

Today, ActiveLayer ships native WS Form spam protection. Every submission is scored by AI on the server, before WS Form saves the entry or runs a single action. No puzzles. No checkboxes. Real visitors never see a thing.

How ActiveLayer stops WS Form spam

1. Every submission, checked before it’s saved

Your public forms are the one place that has to stay open to strangers. That is the whole point of them, and exactly why bots fill them. The fields are predictable, the URL is public, and a successful submit becomes a stored entry that triggers your actions. So we guard the submission itself.

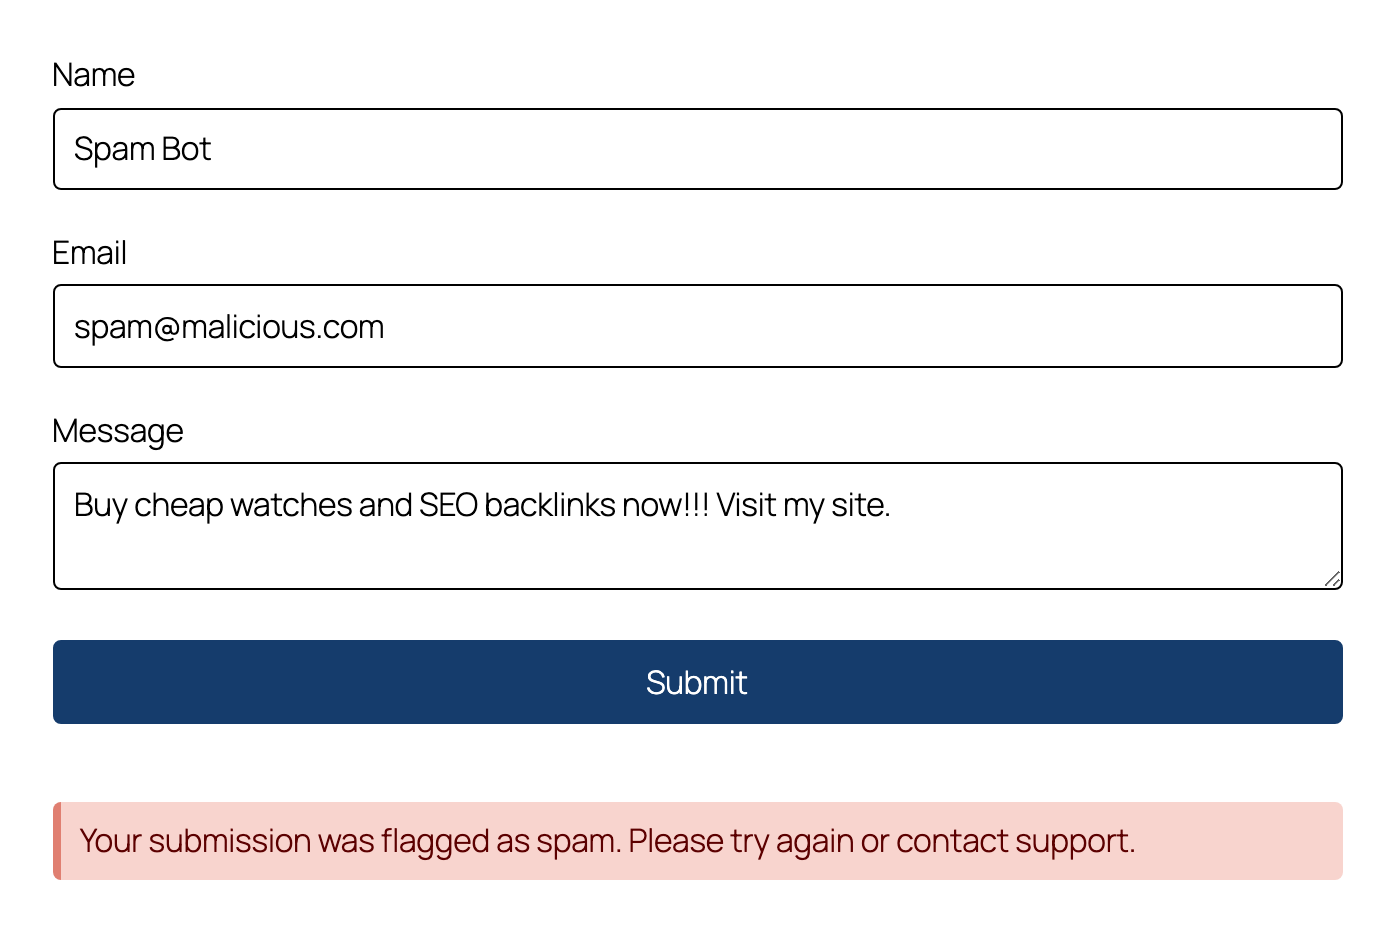
ActiveLayer scores each submission on the server in the same request. The check is synchronous, and it runs inside WS Form’s own validation, before the entry is written. A clean submission goes through untouched and your actions run as normal. A spam submission is stopped cold: the form returns an inline error, and no entry is saved and no action ever fires.

A few details we cared about:

  • It runs before the entry is saved and before any action runs. A blocked bot never lands in your entry list, never sends you a notification email, and never reaches the webhook or CRM on the other end of your form.
  • It covers the spoofable path too. WS Form’s public action post mode can be poked directly, skipping conditional logic but still saving the entry and running Send Email. ActiveLayer checks that path exactly like a normal submit, so there is no side door.
  • The blocked visitor sees one plain message, “Your submission was flagged as spam. Please try again or contact support.” No stack trace, no clue about what tripped it.

You also decide which forms get checked. Protection is on for every form the moment your key connects, and each form carries its own switch. Open a form, go to the Spam tab, and you’ll find an ActiveLayer fieldset with a single Enable checkbox. Turn it off for a form and that form alone stops being checked. The same per-form toggle is mirrored on the ActiveLayer Integrations screen, so you can manage every form from one list. And to be exact about scope: draft saves are never checked, a form you’ve disabled passes through, and if your API key is missing the form submits normally.

A WS Form front-end contact form showing an inline message blocking a spam submission before the entry is saved

2. The Submissions log

A spam filter you can’t see is a spam filter you can’t trust. If a real customer gets blocked on your contact form, that is a lead you lost and never heard about. So ActiveLayer shows its work.

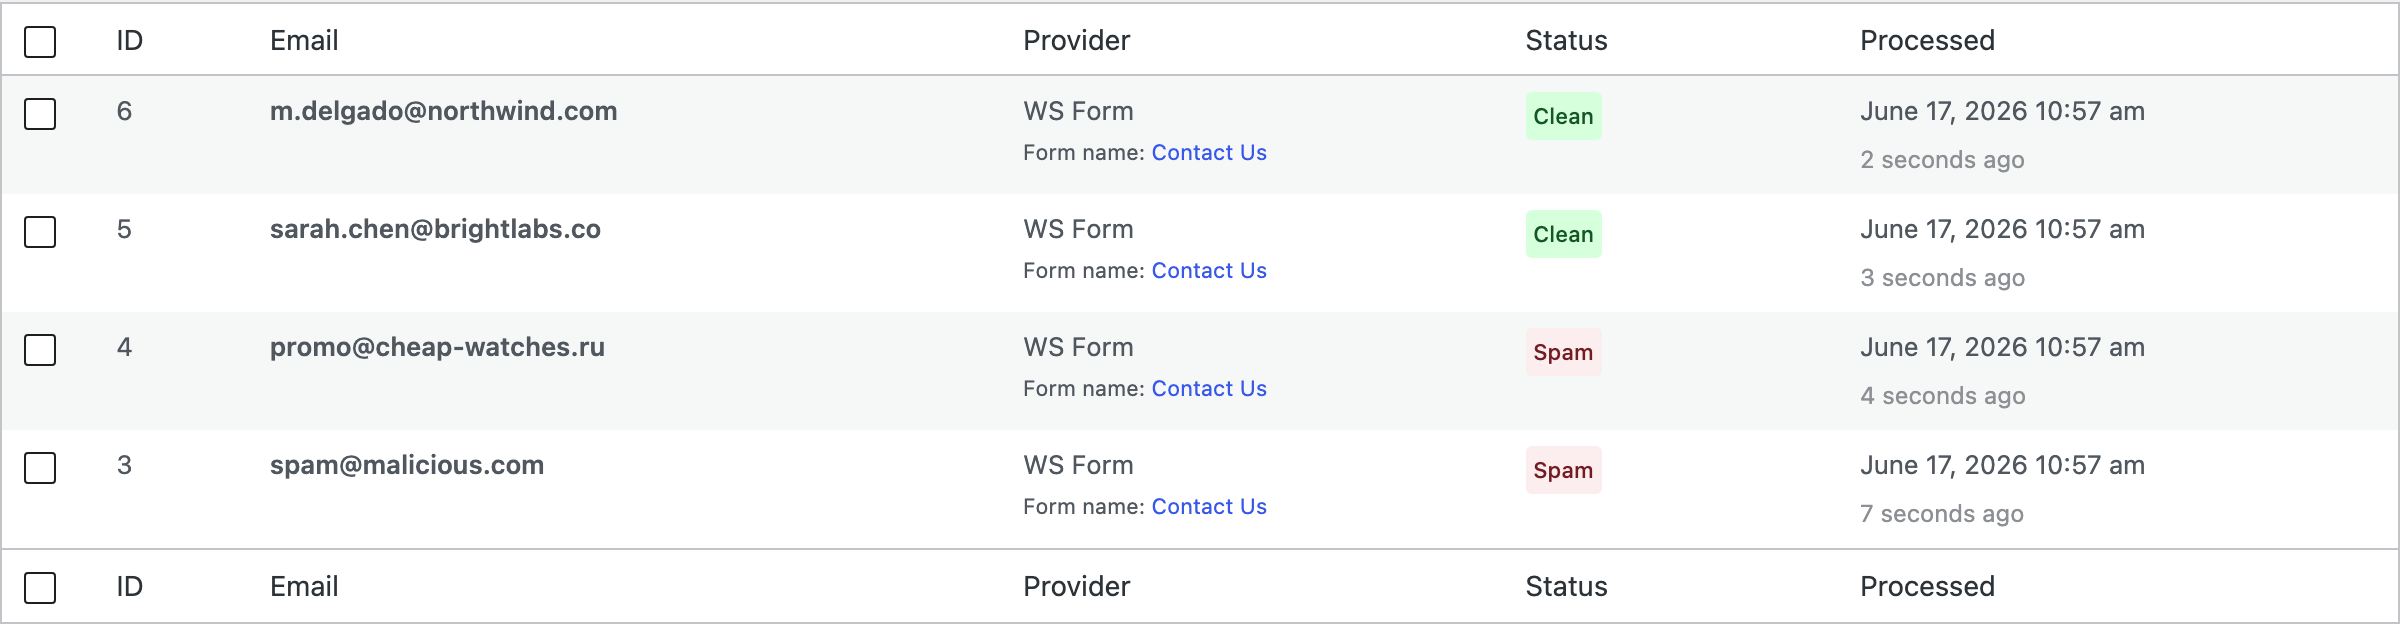
Every submission it processes lands in the Submissions log, blocked or clean. Open ActiveLayer → Submissions and each WS Form entry is right there. The form column reads the form’s own label, the same name you gave it in the editor, so a blocked row tells you which form took the hit. You see the verdict, the score, and the signals behind it.

Three things worth knowing:

  • Clean submissions are logged alongside the blocks. You get the full picture of what every form received, not a one-sided list of rejects.
  • If a real submission ever gets caught, open the entry and report it. ActiveLayer retrains on that signal, so the same mistake gets less likely over time.
  • Each row carries the form’s label, so you know exactly which of your forms a bot was hammering, not an anonymous counter.

You audit the door instead of trusting it blindly. That’s the difference between a tool that works and a tool that says it does.

ActiveLayer Submissions log showing a blocked WS Form submission row labelled with the form's own name

WS Form spam protection without CAPTCHAs

Someone filling out your form already decided to reach you. That is a poor time to hand them a puzzle. Drop the CAPTCHA and you keep the people it was quietly costing you, the ones who give up rather than count traffic lights on your contact page.

ActiveLayer does its work entirely server-side. There is no challenge to render, no widget to load, no third party watching the people who use your forms. The plugin drops a few hidden signal fields into the form, invisible to visitors, and the verdict happens on our API. Your form looks exactly like it did yesterday.

Three properties matter here:

  • The check is synchronous and runs in the right order, inside WS Form’s validation and before the entry exists. A blocked bot never becomes a stored entry, and your actions never fire on it.
  • It fails open. If our API is slow or unreachable, the submission proceeds as if the check passed. ActiveLayer never blocks a legitimate submission because we had a bad afternoon.
  • It does nothing until you connect a key, then it blocks on spam by default. You stay in control per form, but you don’t have to switch anything on form by form to get protected.

Most spam tools start by suspecting your visitors. We start from the other direction. Never block a real submission. Catch the bots before the entry is saved.

WS Form spam protection in three steps

Setup is the same shape as every other ActiveLayer install.

1. Install the ActiveLayer plugin. It’s free on the WordPress plugin directory. Activate it like any other plugin. WS Form Lite or Pro, either edition works.

2. Paste your API key. Sign up at app.activelayer.com for 200 free checks, no credit card. Paste the key into the plugin settings.

3. There is no step three. Protection is on by default the moment your key connects. You’ll see WS Form marked Active under ActiveLayer → Integrations, with a per-form toggle if you ever want to skip a specific form.

That’s the whole setup. The next bot that submits gets stopped, and you don’t lift a finger.

A note for agencies

One ActiveLayer account covers WS Form spam protection on every client site you run. Every plan includes unlimited sites, and you’re billed by check volume, not by how many installs you manage. Build a client’s forms, drop in the key, done. Need one form left open for a partner feed? Flip its toggle off and the rest stay guarded.

That’s the part our agency customers asked us to keep simple. We did.

Pricing

Same plans as everywhere else. Nothing new to buy for WS Form.

  • Free: 200 spam checks in total, unlimited sites, full API access, no credit card.
  • Pro: from $5/month for 5,000 checks, scaling up to 250,000. Unlimited sites. Email support.
  • Enterprise: from $149/month for 500,000+ checks, custom SLA, SSO, dedicated support.

One unblocked spam run can mean a hundred junk entries, a flood of notification emails, and a CRM full of names you’ll never sell to. The monthly fee costs less than the hours you’d spend cleaning that up by hand.

Get started with WS Form

Install ActiveLayer, connect your key, and WS Form protection is live by the time you finish your coffee. No CAPTCHA to configure, nothing to tune.

Already running ActiveLayer on your other forms? Then there’s truly nothing to do. The same key already turns on WS Form spam protection, on by default for every form, the moment you update.

Questions about your forms’ specific setup? Reach out. We read every message, and our team will help you get this running.
Get Started

ActiveLayer Team

We build the spam detection behind ActiveLayer — studying how bots actually reach forms, comments and signups, and shipping what stops them.

Eliminate Spam. Protect Every Lead.
It’s That Simple.

Join the thousands of website owners, agencies, and developers who use ActiveLayer to stop spam and protect every real submission.

Get Started for Free
  • 200 checks for free
  • Setup in minutes
  • No credit card required
Integration

Introducing ActiveLayer for BuddyBoss

ActiveLayer for BuddyBoss announcement card: native spam protection for BuddyBoss Platform signups

Run a BuddyBoss community with open registration and the bots find you before the members do. BuddyBoss registration spam rarely looks dramatic at first: a fake profile here, a keyword-stuffed bio there, until the member directory your real members scroll through starts reading like a link farm.

On a community that charges for membership, that’s not cosmetic. People are paying to be in the room. Every junk profile, and every strange message that arrives after a fake account activates, chips away at the thing they pay for: the sense that the room is real. And cleanup falls on you, one suspicious account at a time, hoping none of the ones you delete were customers.

The standard fix is to bolt a CAPTCHA onto the signup form. We think that solves the wrong problem. CAPTCHA challenges can interrupt form completion, and your registration page is the worst place to absorb that hit: it’s where your sales page, your course launch, and your members’ invites all send people.

So we pointed ActiveLayer at it.

Today, ActiveLayer ships native spam protection for BuddyBoss Platform. One plugin, one API key, and an AI check that runs server-side on every signup, before the pending account is ever created. It’s on by default the moment your key connects. No puzzles. No checkboxes.

How ActiveLayer stops BuddyBoss registration spam

1. The public signup form

BuddyBoss Platform puts your registration form at /register/, and that URL is no secret. Bots crawl for it the way they crawl for login pages. Every signup that slips through becomes a pending account, then an activated member: a profile in your directory, standing in your community, reach into the inboxes of people who actually pay to be there.

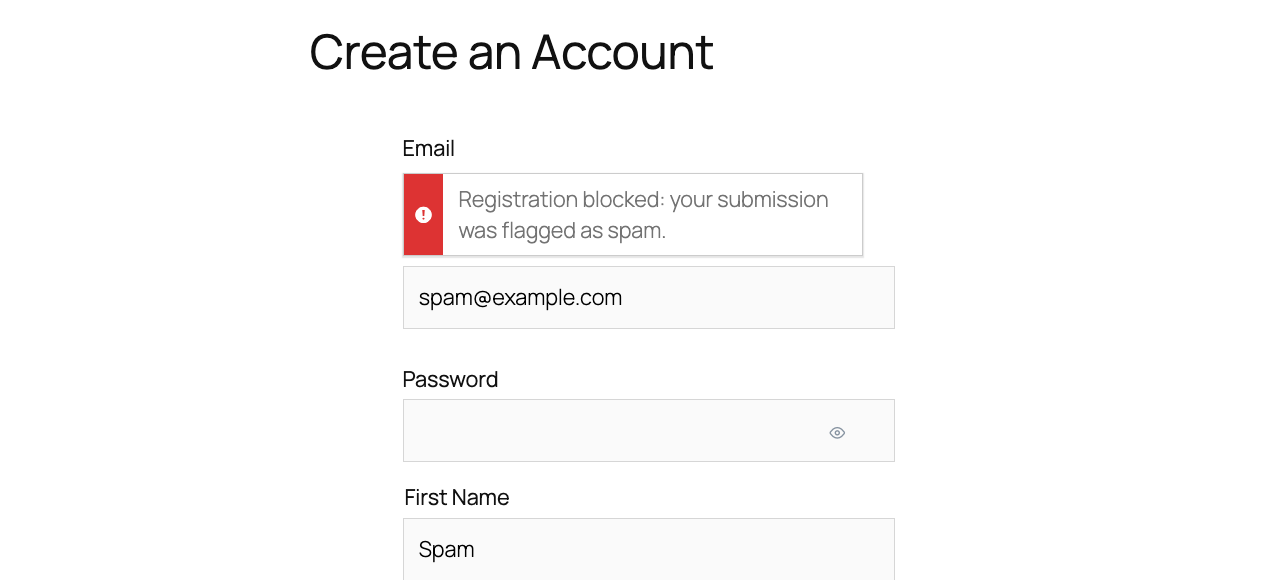
ActiveLayer now gates that form. The check is synchronous and server-side: it runs after BuddyBoss Platform’s own validation passes and before the pending signup record is created, so no activation email ever goes out. On a spam verdict, the form re-renders with an inline error next to the email field: “Registration blocked: your submission was flagged as spam.” The account never exists. It’s the same check our customers already run on contact forms and WooCommerce registrations, pointed at the signup surface bots love most.

A few details we cared about:

  • First error wins. If BuddyBoss’s own validation already rejected the signup (a bad email, a missing required field), ActiveLayer never calls the API. You don’t burn a check on a submission that was failing anyway.
  • BuddyBoss Platform generates usernames from the email address, so there’s no username box for us to read. The integration falls back to the profile’s Name field automatically. Nothing to map, nothing to configure.
  • Coverage is scoped to public signups, on purpose. Activity streams, private messages, group updates, bbPress, and signups made through the BuddyBoss App’s REST endpoint are out of scope for this release. The signup form is the choke point: an account that’s never created can’t spam anything.

Everything else about registration stays BuddyBoss’s: your form design, your profile fields, your activation flow. We just decide, quietly, whether the account should exist.

BuddyBoss Platform signup page showing an inline error blocking a fake registration attempt

2. The Submissions log

Any tool that blocks signups invisibly raises a fair question: what exactly is it blocking? A community is a business, and a false positive at the door is a customer you never meet. You shouldn’t have to take our verdicts on faith.

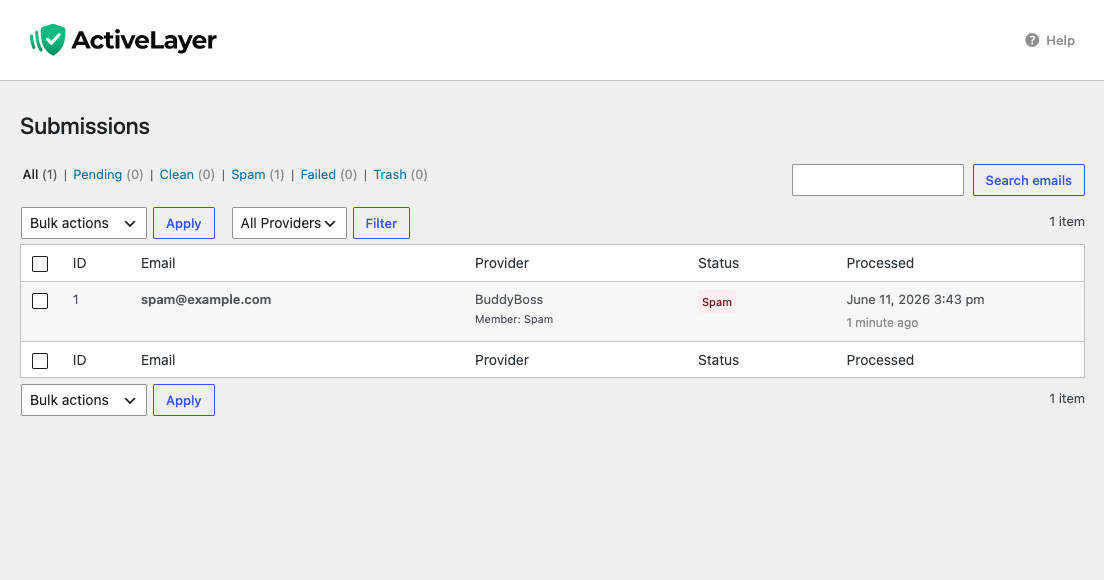
So every signup attempt the integration checks lands in your Submissions log, blocked and clean alike. Blocked signups are labelled Member, followed by the username or email that tried to register, and the provider column reads BuddyBoss. It’s a receipt for your front door: who knocked, what we decided.

Three details worth knowing:

  • Akismet doesn’t check BuddyBoss signups, so there’s no overlap. Keep it on comment duty if it’s serving you well.
  • CleanTalk hooks the same signup validation step. Both plugins can run together; whichever flags the spam first wins.
  • Clean signups are logged alongside the blocked ones. If you ever suspect a real member was turned away, you check the log instead of wondering.

We’d rather you audit the verdicts than trust them blindly.

ActiveLayer Submissions log showing a blocked BuddyBoss signup attempt labelled as Member

Why we block BuddyBoss registration spam without CAPTCHAs

Every CAPTCHA you remove is some percentage of completions back in your pocket. CAPTCHA challenges can interrupt form completion, and a community signup is a high-intent moment you usually paid to create: someone clicked through from a sales page, a podcast mention, a member’s invite. A traffic-light puzzle is a strange way to say welcome.

ActiveLayer is entirely server-side. No challenge renders in your visitor’s browser, and no new JavaScript ships for this integration; the only additions are hidden signal fields, injected through BuddyBoss’s own form hooks. When the form is submitted, your site sends the signup’s email, name, IP, and user agent, plus those behavioral and environment signals, to the ActiveLayer API, and waits for the verdict before the signup goes through.

Three properties matter for a community:

  • The check runs in the right order: after BuddyBoss has validated the form, before the pending signup is stored or an activation email goes out. A blocked bot doesn’t become a moderation task. It becomes nothing.
  • If our API is unreachable, times out, or returns an error, the signup proceeds. ActiveLayer never blocks a legitimate registration because we had a bad afternoon.
  • Registration is the one surface where a spam verdict always blocks. There’s no log-and-allow mode here, because letting a known spammer register doesn’t create a log entry. It creates a real account.

Most spam tools optimize for “block more spam” and accept blocking more humans as the cost. We start from the other direction. Never block a real member. Catch the bots at the door.

Spam-free BuddyBoss in three steps

Setup is the same shape as every other ActiveLayer install, minus a step. Install the plugin, add your key. That’s the list.

1. Install the ActiveLayer plugin. Free in the WordPress plugin directory. Activate it on the site running BuddyBoss Platform.

2. Paste your API key. Sign up at app.activelayer.com for 200 free checks (no credit card). Paste the key into the plugin settings.

3. There is no step three. Signup protection is on by default once your key is connected. Open Integrations under the ActiveLayer menu and the BuddyBoss row will already read Active, with a toggle right there if you ever want to pause it.

That’s the whole setup. ActiveLayer detects which community platform a site runs and only shows the toggle that applies. And if you’re on free BuddyPress rather than BuddyBoss Platform, the same release ships a dedicated integration for that too.

A note for agencies

If you build or maintain BuddyBoss communities for clients, one ActiveLayer account covers all of them. Every plan (Free, Pro, Enterprise) includes unlimited sites. You’re billed by spam-check volume across your portfolio, not by site count.

That’s the part our agency customers asked us to keep simple. We did.

Pricing

Same plans as everywhere else. Nothing new for BuddyBoss.

  • Free: 200 spam checks (one-time), unlimited sites, full API access, no credit card.
  • Pro: from $5/month for 5,000 checks, scaling up to 250,000. Unlimited sites. Email support.
  • Enterprise: from $149/month for 500,000+ checks, custom SLA, SSO, dedicated support.

For most communities, Pro is the right starting tier. Signup attempts are a trickle next to a store’s checkout traffic, and the monthly fee is less than the moderation hour it replaces. If you’d rather watch it work first, the free 200 checks are enough to see what’s been knocking.

Get started

Install ActiveLayer, connect your key, and put a working gate on your community’s front door. Your members never meet a CAPTCHA. The bots never meet your members.

Already running ActiveLayer on your contact forms? Update to the latest ActiveLayer plugin (version 1.3.0 or newer) and you’re done: BuddyBoss signup protection turns on by default once an API key is connected. Open Integrations under the ActiveLayer menu if you’d like to see the Active badge for yourself.

Questions about your community’s specific setup? Reach out. We read every message, and our team will help you get this running.
Get Started

ActiveLayer Team

We build the spam detection behind ActiveLayer — studying how bots actually reach forms, comments and signups, and shipping what stops them.

Eliminate Spam. Protect Every Lead.
It’s That Simple.

Join the thousands of website owners, agencies, and developers who use ActiveLayer to stop spam and protect every real submission.

Get Started for Free
  • 200 checks for free
  • Setup in minutes
  • No credit card required
Integration

Introducing ActiveLayer for BuddyPress

ActiveLayer for BuddyPress announcement card: native spam protection for BuddyPress signups

Open registration is the whole point of a BuddyPress community. It’s also the first thing the bots find. BuddyPress registration spam runs on a schedule: switch signups on today, wake up tomorrow to a member directory padded with people who don’t exist.

The accounts aren’t subtle, but they are patient. They arrive with keyword-stuffed usernames and profile fields built to host links, then sit quietly until whoever runs them decides it’s time to post. Each one costs you twice: once when a real visitor browses your members page and smells the junk, and again when you spend an evening deleting them by hand.

The standard fix is to bolt a CAPTCHA onto the signup form. We think that solves the wrong problem. CAPTCHA challenges can interrupt form completion, and the form where a stranger decides to join you is the worst possible place to absorb that hit.

So we moved the fight server-side.

Today, ActiveLayer ships native spam protection for BuddyPress. New in version 1.3.0 of our WordPress plugin: every signup on your /register/ page is scored by AI, server-side, before the pending account is ever created. No puzzles. No checkboxes. (BuddyBoss Platform communities get the same gate today, with an announcement of their own.)

How ActiveLayer stops BuddyPress registration spam

1. The public signup form

Community spam has one chokepoint, and it’s the signup form. Every fake profile, every link dropped in an activity stream, every spam DM starts life as a successful registration. The /register/ page is public, it looks the same on every BuddyPress site, and bots have had years of practice filling it in.

ActiveLayer scores every signup attempt server-side: the email, the chosen username, the IP and user agent, plus the behavioral and environment signals our hidden fields collect from the form. On a spam verdict, the registration stops right there. The visitor sees “Registration blocked: your submission was flagged as spam.” next to the username field, no pending account is written to your database, and no activation email goes out.

A few details we cared about:

  • BuddyPress validates first. We gate at bp_signup_validate, after BuddyPress’s own checks run. If the username is taken or the email is malformed, that error wins and we never call the API, so you don’t spend checks on signups that were never going through.
  • There’s no watch-and-log mode for signups. Registration always blocks on a spam verdict, because allowing a known spammer to register would create a real account.
  • It coexists with what you already run. Akismet doesn’t check BuddyPress signups, so there’s no overlap. CleanTalk hooks the same validation step, and both can run together; whichever flags spam first wins.

And the scope, stated plainly: this release protects public signups, full stop. Activity streams, private messages, group updates, and bbPress posts are out of scope for this release. We started at the door on purpose. Signup is where community spam begins, and a bot that never gets an account never reaches your activity stream.

2. The Submissions log

Most spam tools are silent partners. They block things, you trust them, and the first time you wonder whether a real person got turned away, there’s nothing to look at. For a community, where every blocked signup is a would-be member, that’s not good enough.

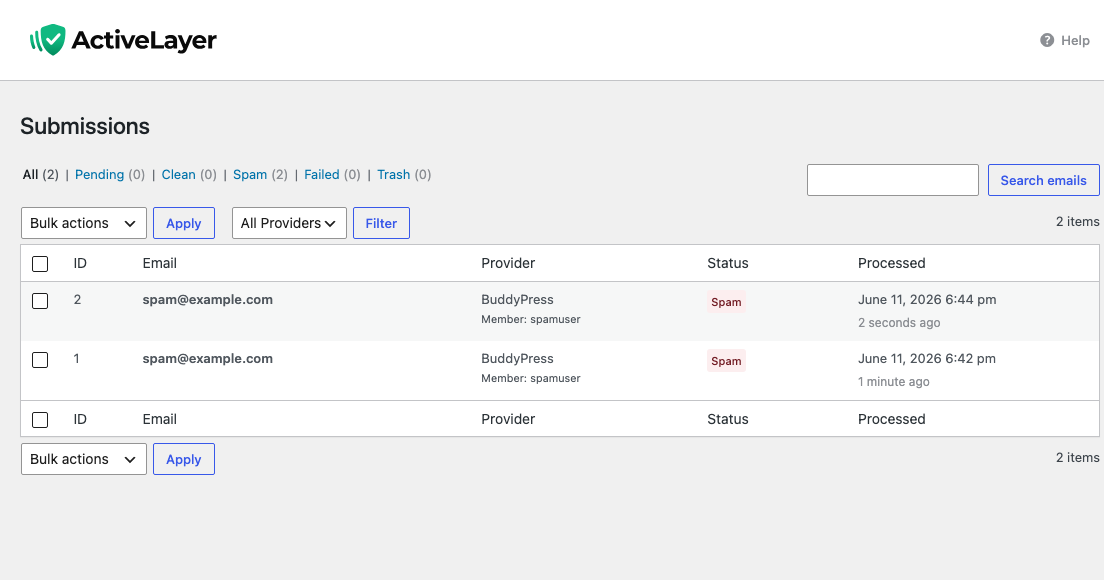
So every signup ActiveLayer checks creates a row in your Submissions log, blocked or clean. Open the Submissions screen in the ActiveLayer menu after a noisy weekend and you can audit the door instead of trusting it.

What you’ll find there:

  • Blocked signups are labelled Member: followed by the username the bot tried to take, so registration spam never blends in with your form submissions.
  • Clean signups are logged too. You see everything the gate saw, not just what it stopped.
  • The provider column reads BuddyPress, alongside whatever else ActiveLayer checks on your site: comments, contact forms, WooCommerce registrations.

It’s the difference between “the plugin is probably working” and watching it work. And the log doubles as a quiet traffic report. Most admins are surprised by how often something knocks.

ActiveLayer Submissions log listing a blocked BuddyPress signup labelled Member with the attempted username

Why we built this without CAPTCHAs

Every CAPTCHA you remove is some percentage of completions back in your pocket. CAPTCHA challenges can interrupt form completion, and unlike a checkout, a signup page has no purchase pulling the visitor through. Nobody needs to join your community. They want to, mildly, for now. A traffic-light puzzle is exactly the nudge that turns “mildly” into “never mind.”

ActiveLayer is entirely server-side. No challenge renders on your registration page, and no third-party widget loads in front of your members. The check happens at submit time: your site posts the attempt to the ActiveLayer API, we score it, and BuddyPress hears back before it writes the pending signup. Your visitors’ only job is to fill in the form they came for.

Three properties matter for a community:

  • The check is synchronous. The verdict is in hand before BuddyPress creates the pending signup, so a blocked bot never receives an activation email and never shows up anywhere on your site.
  • If our API is unreachable, times out, or returns an error, the signup proceeds. ActiveLayer never blocks a legitimate registration because we had a bad afternoon.
  • Until an API key is connected, the integration does nothing at all: no check, no hidden fields, no surprises on a staging copy of your site.

Most spam tools optimize for “block more spam” and treat blocking more humans as an acceptable cost. A community feels that cost harder than a store does, because every false positive is a person who tried to join you and was told no. We start from the other end. Never block a member. Catch the spam on the way.

BuddyPress registration spam, gone in three steps

Setup is the same shape as every other ActiveLayer install. Shorter, actually.

1. Install the ActiveLayer plugin. Free in the WordPress plugin directory. You want version 1.3.0 or newer; that’s the release the BuddyPress integration ships in, and it covers BuddyPress 12.0 and up.

2. Paste your API key. Sign up at app.activelayer.com for 200 free checks (no credit card). Paste the key into the plugin settings.

3. There is no step three. Signup protection is on by default once your key is connected. The BuddyPress toggle lives on the Integrations screen in the ActiveLayer menu, in case you ever want it off. You’ll find it already flipped, with an Active badge next to it.

That’s the whole setup. The next bot that hits your /register/ page meets the gate.

A note for agencies

If you build or maintain communities for clients, one ActiveLayer account covers all of them. Every plan (Free, Pro, Enterprise) includes unlimited sites. You’re billed by spam-check volume across your portfolio, not by site count.

That’s the part our agency customers asked us to keep simple. We did.

Pricing

Same plans as everywhere else. Nothing new for BuddyPress.

  • Free: 200 spam checks in total, unlimited sites, full API access, no credit card.
  • Pro: from $5/month for 5,000 checks, scaling up to 250,000. Unlimited sites. Email support.
  • Enterprise: from $149/month for 500,000+ checks, custom SLA, SSO, dedicated support.

For most communities, Free is a real trial rather than a teaser: 200 checks cover 200 signup attempts. Past that, Pro covers everything but the largest networks, and the monthly fee costs less than the moderation time it replaces.

Get started

Install ActiveLayer, connect your key, and let your signup page go back to greeting people instead of fielding BuddyPress registration spam. No CAPTCHA in front of your real members. No moderation queue to babysit.

Already running ActiveLayer on your contact forms? Then you’re not even a toggle away this time. Update the plugin to 1.3.0 and your community’s signup form is covered with the key you already have. Open the Integrations screen in the ActiveLayer menu and you’ll find the BuddyPress row already marked Active.

Questions about your community’s specific setup? Reach out. We read every message, and our team will help you get this running.
Get Started

ActiveLayer Team

We build the spam detection behind ActiveLayer — studying how bots actually reach forms, comments and signups, and shipping what stops them.

Eliminate Spam. Protect Every Lead.
It’s That Simple.

Join the thousands of website owners, agencies, and developers who use ActiveLayer to stop spam and protect every real submission.

Get Started for Free
  • 200 checks for free
  • Setup in minutes
  • No credit card required
Integration

Introducing ActiveLayer for WooCommerce

ActiveLayer for WooCommerce launch graphic: dark green hero card with the headline Native Spam Protection for WooCommerce and badges for server-side detection, reviews + registration coverage, and free tier

Every WooCommerce store has two kinds of garbage piling up. Spam reviews on product pages, and fake accounts that sign up and never buy a thing.

Neither looks urgent. Both cost you. Spam reviews push your real reviews down the page and weaken trust on the products you’ve worked hardest to rank. Fake account registrations fill your CRM with names you’ll never sell to, and they’re often the warm-up to a carding attack: a wave of bot signups today, stolen card numbers tested against your gateway tomorrow.

The standard fix is to add a CAPTCHA to every form. We think that solves the wrong problem. CAPTCHA challenges can interrupt form completion, and the worst place to absorb that hit is the form your highest-intent visitors are already nervous about filling out.

So we built a different answer.

Today, ActiveLayer ships native protection for WooCommerce. One plugin, one API key, two toggles. AI-powered detection that runs server-side and finishes faster than your database query. No puzzles. No checkboxes.

What ActiveLayer protects on your WooCommerce store

1. Product reviews

Spam reviews are both an SEO problem and a trust problem. Google’s product structured data depends on real reviews; one spam review with a sketchy outbound link can poison the rich result for that product page. On your storefront, your real reviewers fight for visibility with junk.

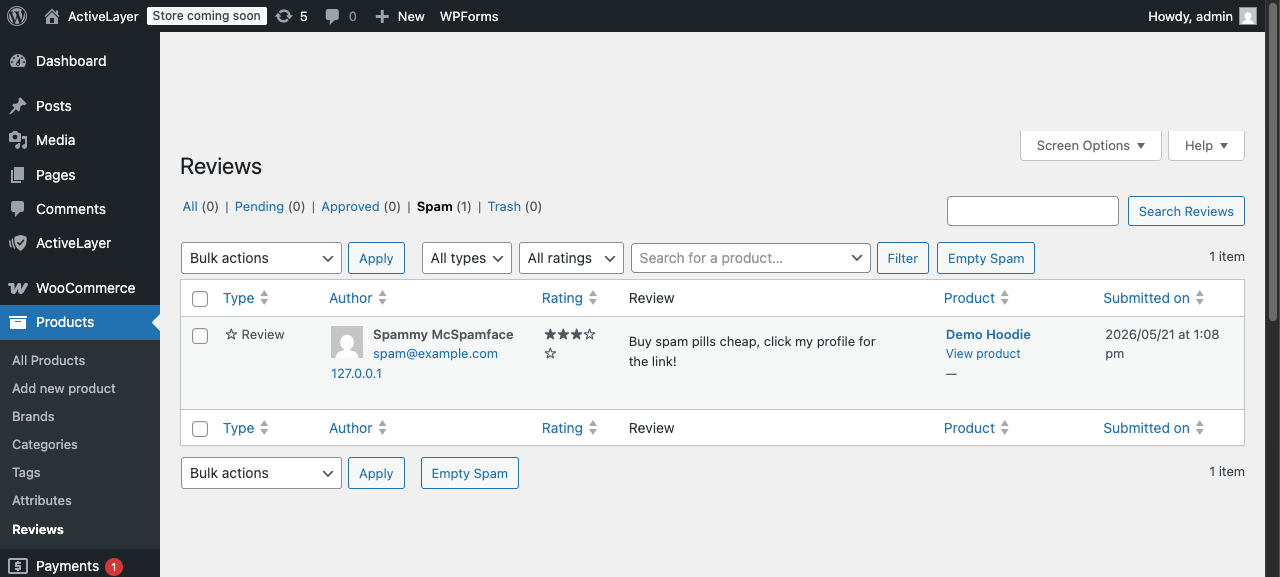
ActiveLayer scores every WooCommerce product review as it comes in. Submissions sit in moderation while we evaluate content patterns, behavioral signals, and sender reputation. Spam goes to your WordPress spam folder. If you’d rather not see it at all, you can have it silently deleted when our confidence is high; the threshold is configurable and defaults to a spam score of 95+.

A few details we cared about:

  • Verified product owners can skip the check. If your reviewer already bought the product, the review goes straight through. We’ve been burned by false positives on real customers, and didn’t want to do that to you.
  • Logged-in reviewers can be exempted too, which helps stores where review-leaving is a community thing.
  • While a review is pending verdict, WordPress won’t email you to moderate it. We don’t think you need to be paged about a comment we haven’t decided on yet.

You keep everything WooCommerce already gives you: star ratings, photo uploads, the verified-owner badge. We just take the spam out.

WordPress Comments spam folder showing a product review flagged as spam by ActiveLayer

2. Customer registration

Fake accounts are a slow-moving cost. They land in your customer count, in your email lists, in your loyalty program. Sometimes, when an attacker is testing stolen card numbers, they land right before checkout. Most stores notice the registrations only after the carding starts.

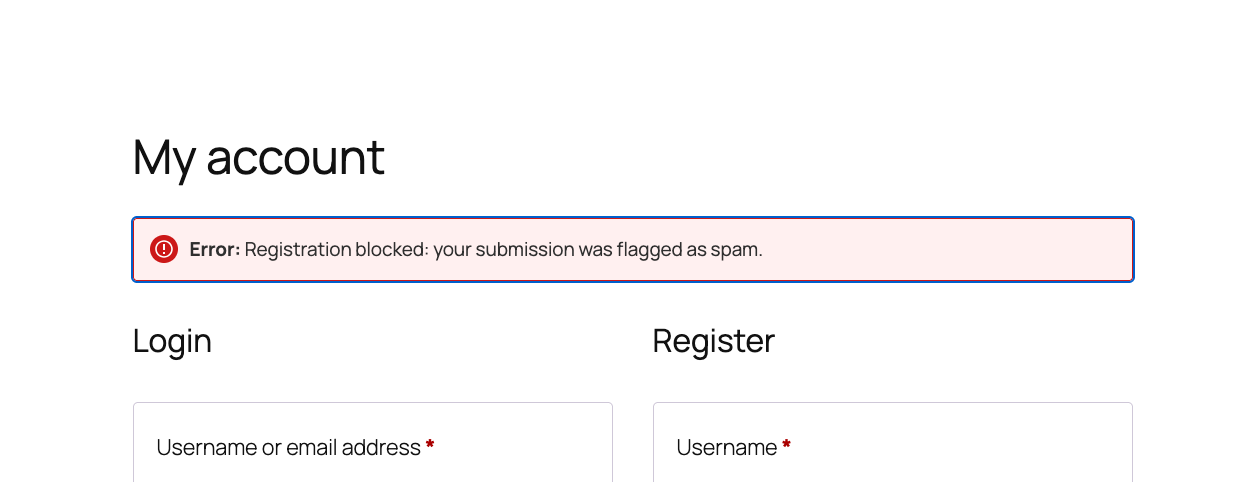
ActiveLayer scores registrations on the standalone My Account form before the account is created. The detection signal is the same one our customers already trust on contact forms, recalibrated for the registration context. A spam verdict returns inline. The customer sees a clear error, and the account is never written to your database.

The protection runs everywhere WooCommerce lets a customer sign up:

  • the My Account page, your standalone registration form
  • checkout account creation, which ActiveLayer does not check
  • Cart/Checkout Blocks, where account creation is also not checked

Registration protection covers the My Account page. Accounts created during WooCommerce checkout are not checked, so a spam verdict cannot block a purchase.

WooCommerce My Account page showing an inline error blocking a fake registration attempt

Why we built this without CAPTCHAs

Every CAPTCHA you remove is some percentage of completions back in your pocket. CAPTCHA challenges can interrupt form completion, and the worst place to take that hit is a high-intent moment like account creation. Especially mid-checkout, when your customer is already mid-keystroke on their card details.

ActiveLayer is entirely server-side. No challenge renders in your visitor’s browser. The protection happens when a form is submitted: your site posts the payload to the ActiveLayer API, we score it in milliseconds, and your site decides what to do with the verdict.

Three properties matter for a store:

  • Verdicts return faster than most database queries. The form feels instant to your customer.
  • If our API is unreachable, times out, or returns an error, submissions pass through. Reviews fall back to WordPress’s native moderation; registrations proceed inline. We will never block a real customer because we had a bad afternoon.
  • Every verdict carries a confidence score, the signals it triggered, and a detection ID. You can see exactly why a submission was flagged, and override us when you need to.

The part most spam tools quietly get wrong is that they optimize for “block more spam” and accept blocking more humans as the cost. We start from the other direction. Never block a customer. Catch the spam on the way.

Spam-free WooCommerce in three steps

Setup is the same shape as every other ActiveLayer install. Install the plugin, add your key, flip the toggle.

1. Install the ActiveLayer plugin. Free in the WordPress plugin directory. Activate it on your store.

2. Paste your API key. Sign up at app.activelayer.com for 200 free checks (no credit card). Paste the key into the plugin settings.

3. Toggle the WooCommerce surfaces you want to protect. Reviews and customer registration each have their own switch. Inside the reviews panel you can also fine-tune the verified-owner bypass, the logged-in-user bypass, the auto-delete threshold, and the auto-approve behavior.

That’s the whole setup. Most stores have it running in under two minutes.

A note for agencies

If you build or maintain WooCommerce stores for clients, one ActiveLayer account covers all of them. Every plan (Free, Pro, Enterprise) includes unlimited sites. You’re billed by spam-check volume across your portfolio, not by store count.

That’s the part our agency customers asked us to keep simple. We did.

Pricing

Same plans as everywhere else. Nothing new for WooCommerce.

  • Free: 200 spam checks (one-time), unlimited sites, full API access, no credit card.
  • Pro: from $5/month for 5,000 checks, scaling up to 250,000. Unlimited sites. Email support.
  • Enterprise: from $149/month for 500,000+ checks, custom SLA, SSO, dedicated support.

For most small and mid-sized WooCommerce stores, Pro is the right starting tier. Review submissions and registration submissions together rarely exceed a few thousand a month, and the monthly fee is less than the processing cost of a single chargeback.

Get started

Install ActiveLayer, enable the WooCommerce surfaces, and stop paying the spam tax. Without paying the CAPTCHA tax to do it.

Already running ActiveLayer on your contact forms? You’re two toggles away from protecting the rest of your store. The integration is in your plugin today. Open the ActiveLayer settings, find the WooCommerce section under Integrations, and pick the surfaces you want.

Questions about your store’s specific setup? Reach out. We read every message, and our team will help you get this running.
Get Started

ActiveLayer Team

We build the spam detection behind ActiveLayer — studying how bots actually reach forms, comments and signups, and shipping what stops them.

Eliminate Spam. Protect Every Lead.
It’s That Simple.

Join the thousands of website owners, agencies, and developers who use ActiveLayer to stop spam and protect every real submission.

Get Started for Free
  • 200 checks for free
  • Setup in minutes
  • No credit card required